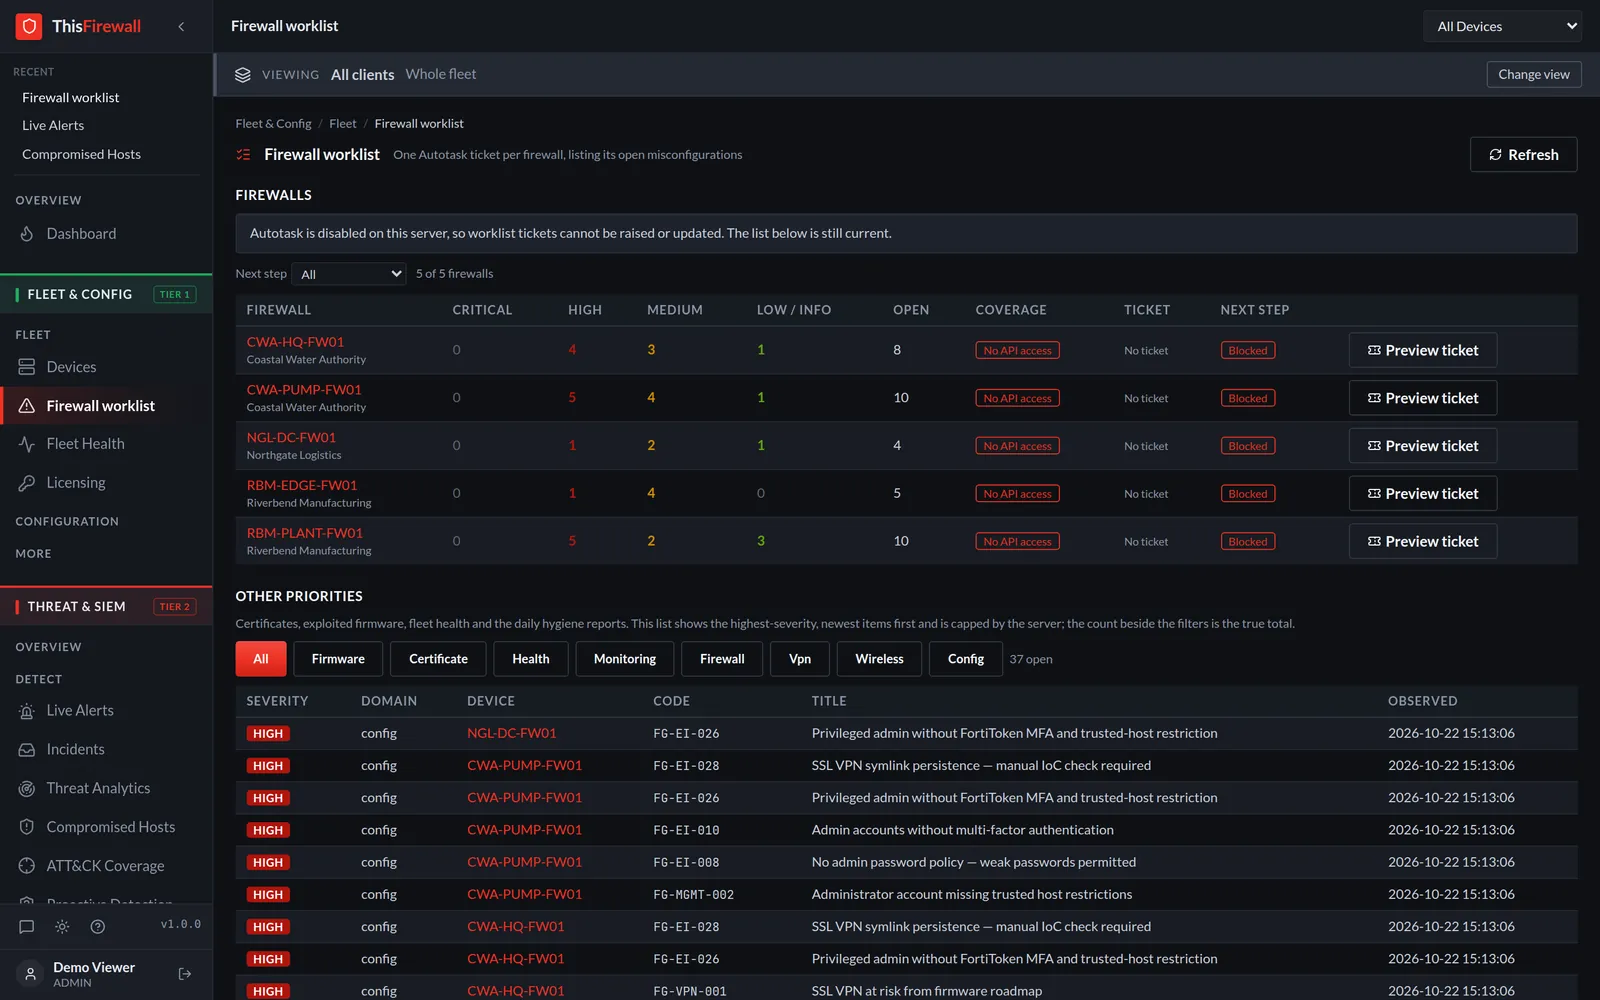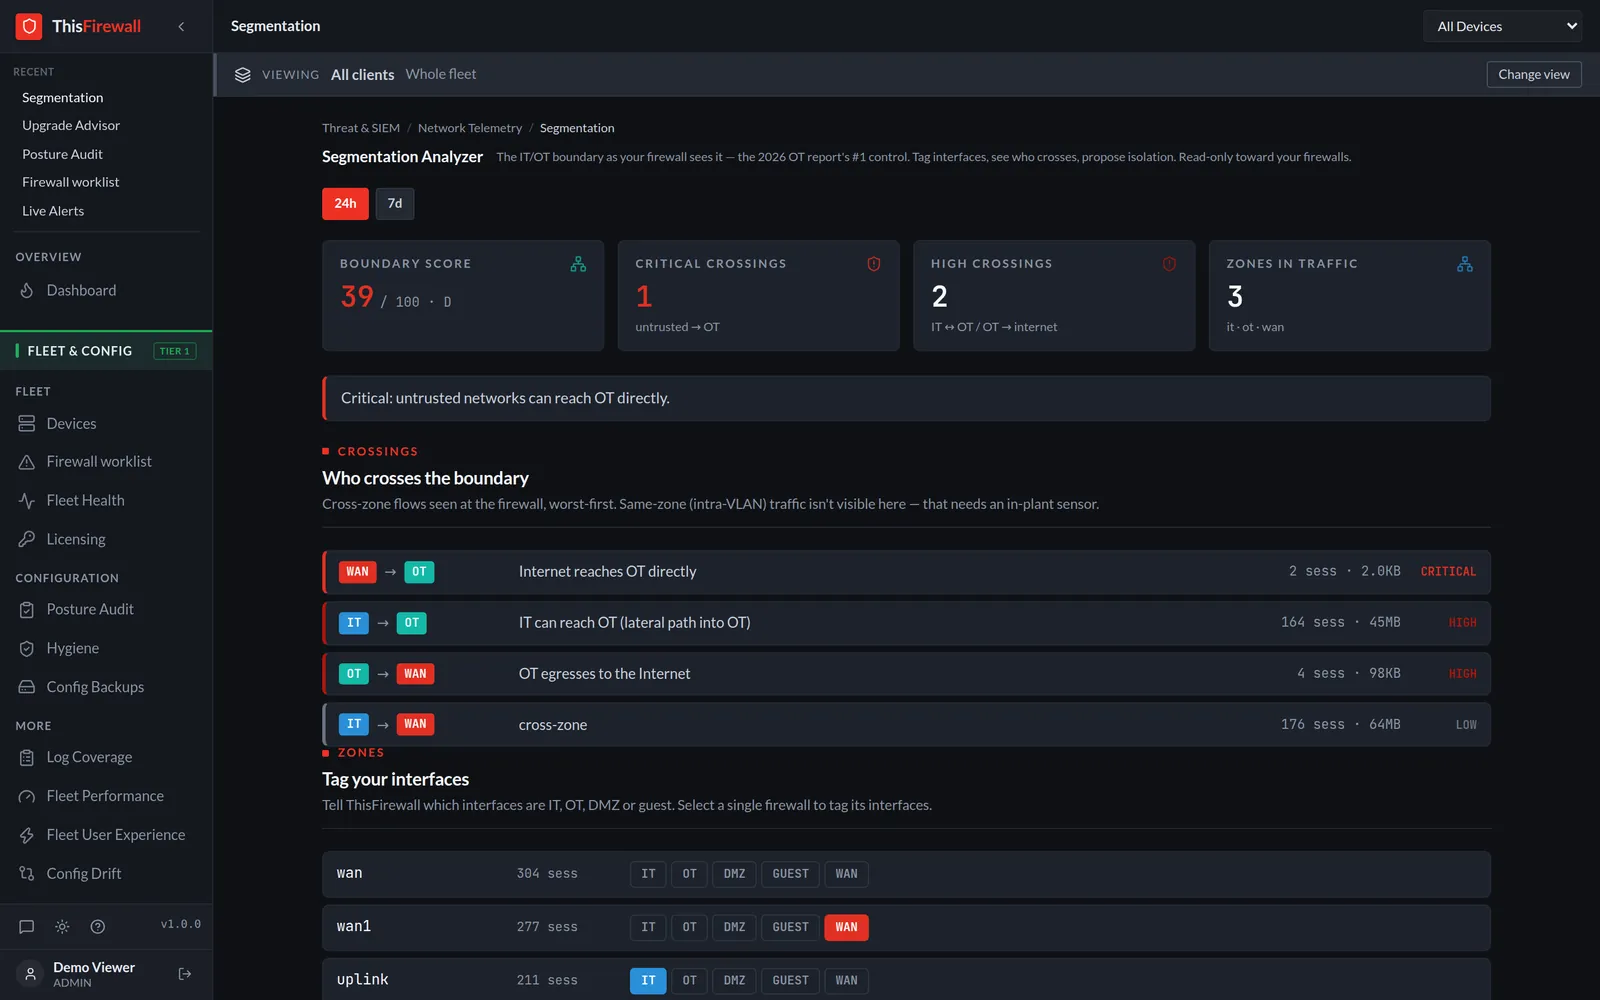
Nobody reads the logs.
Every firewall logs every session it handles. Across a fleet that is far more than anyone can read, so the connection your policy allowed sits there unread.
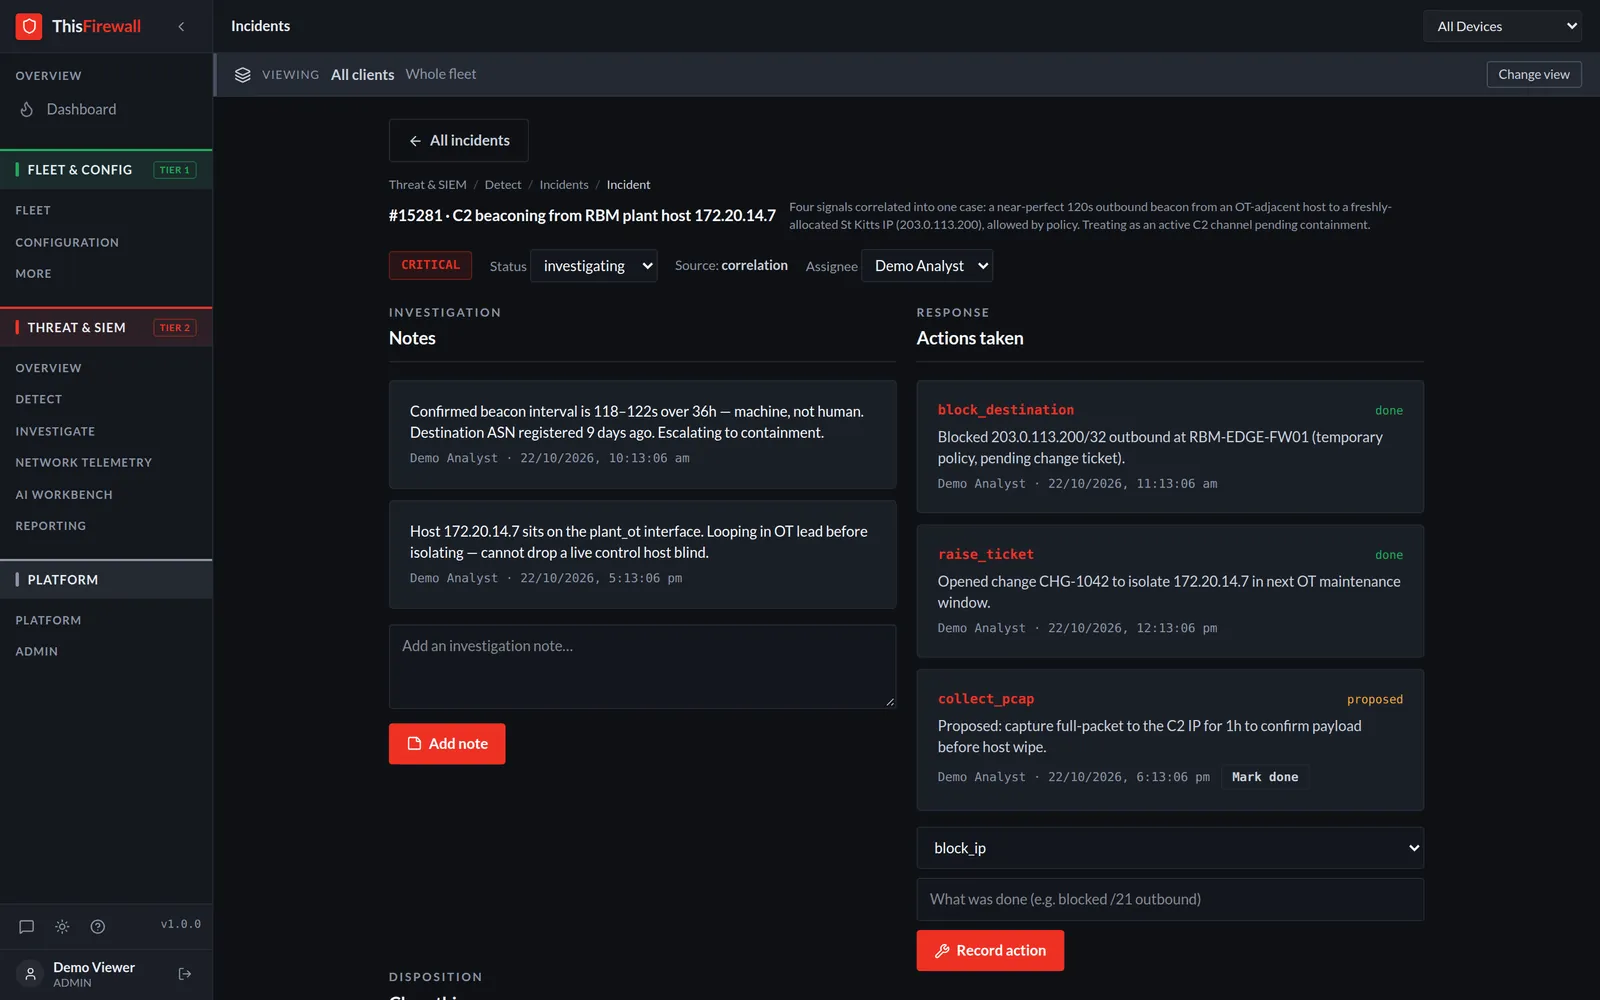
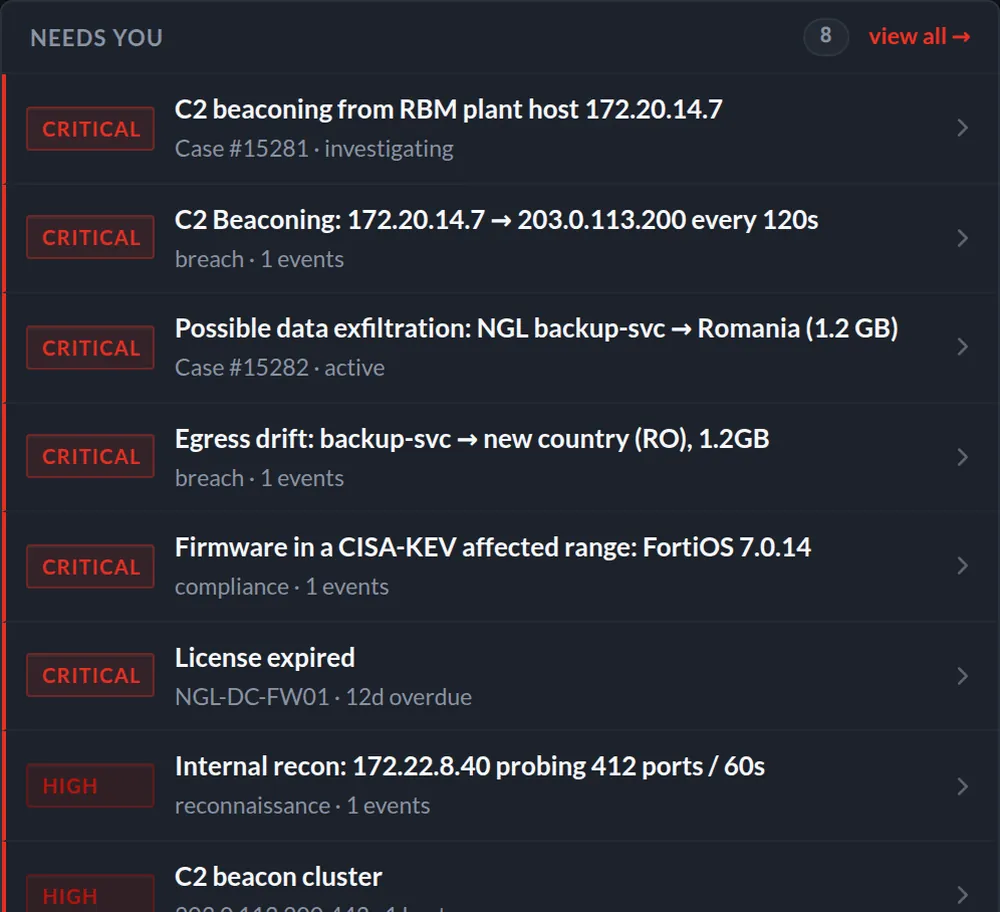
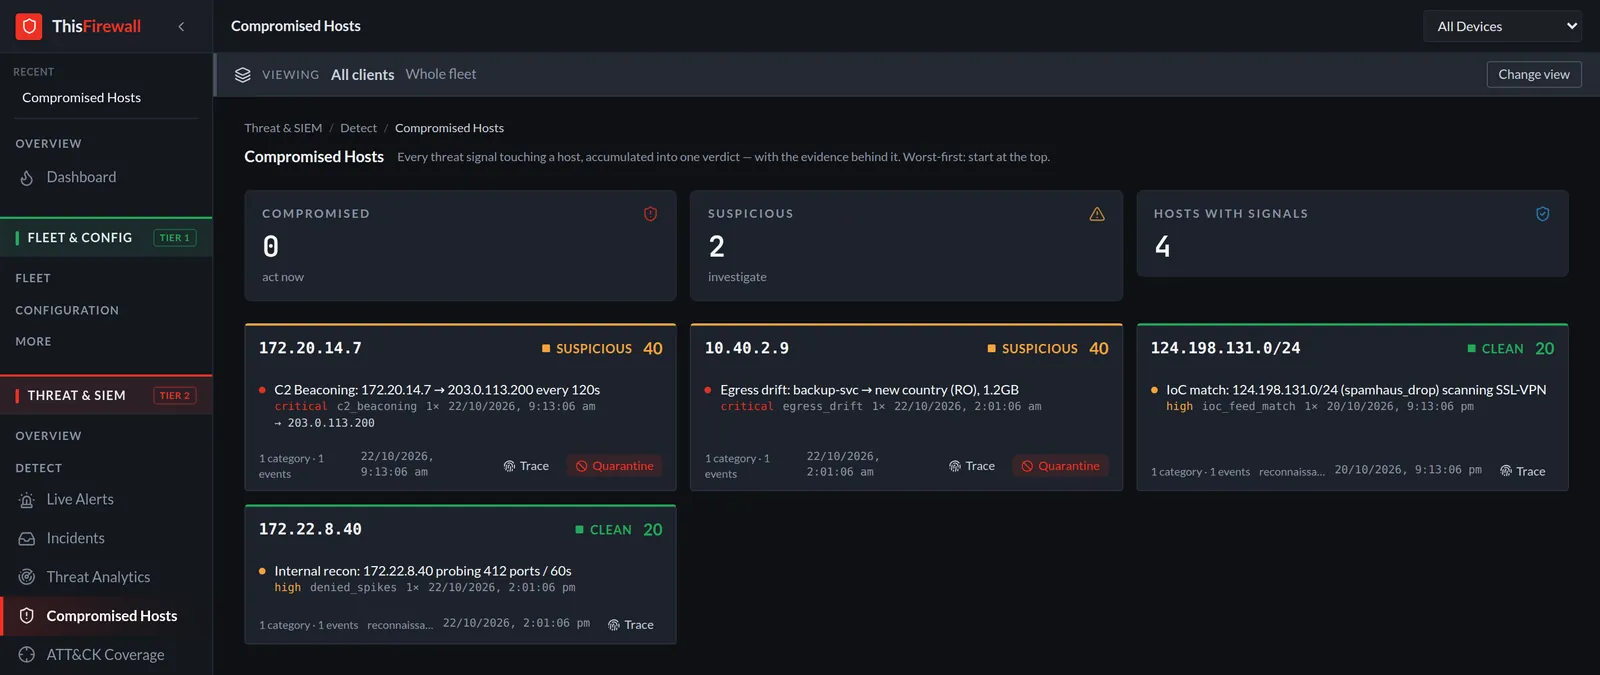
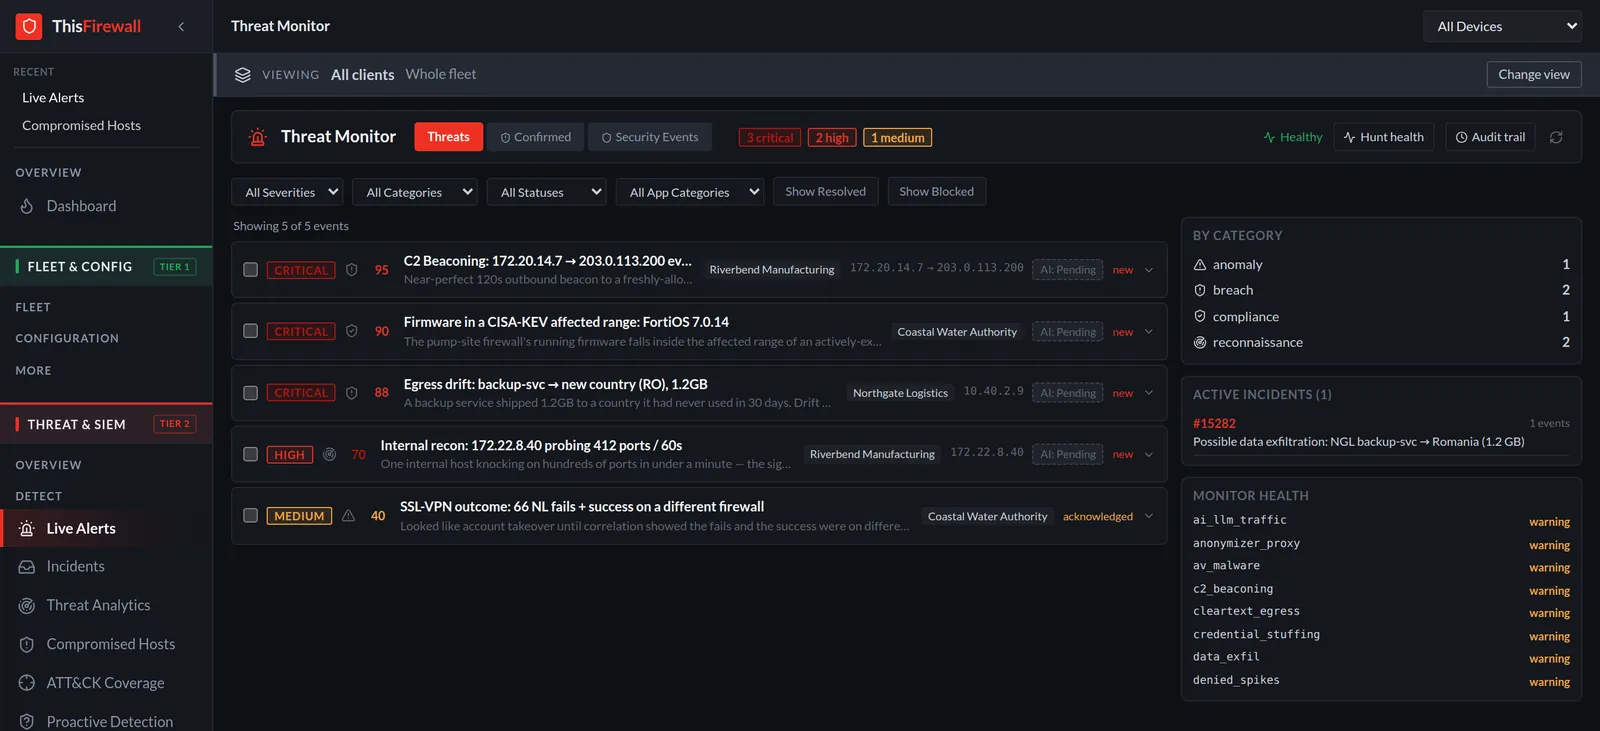
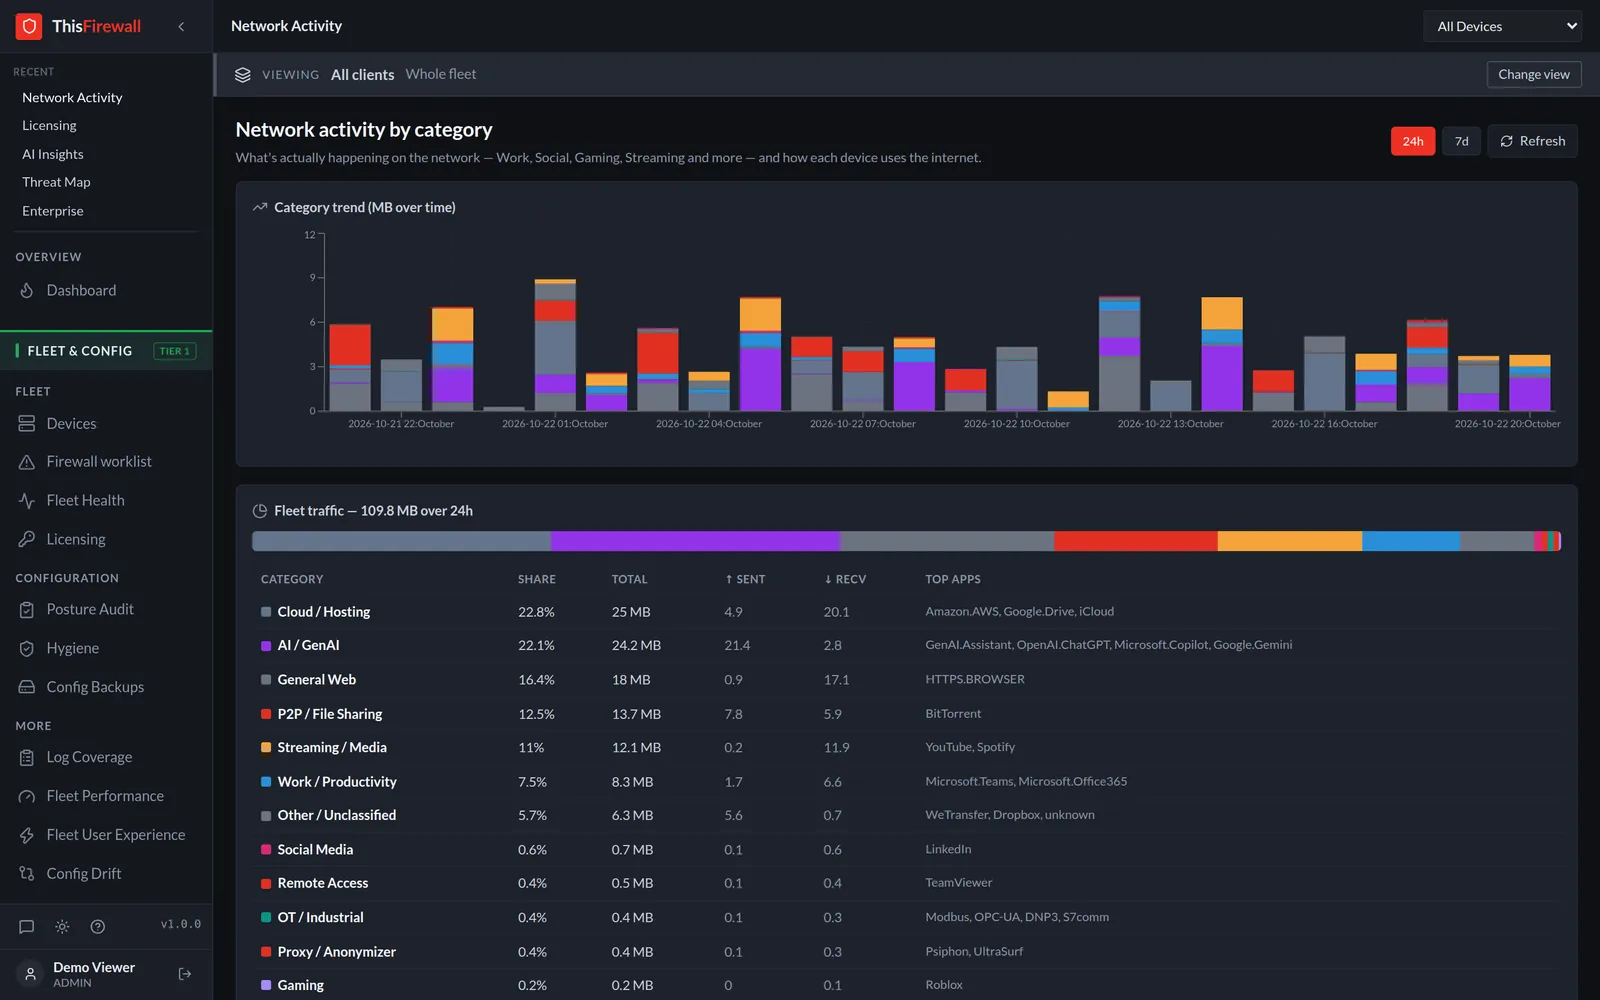
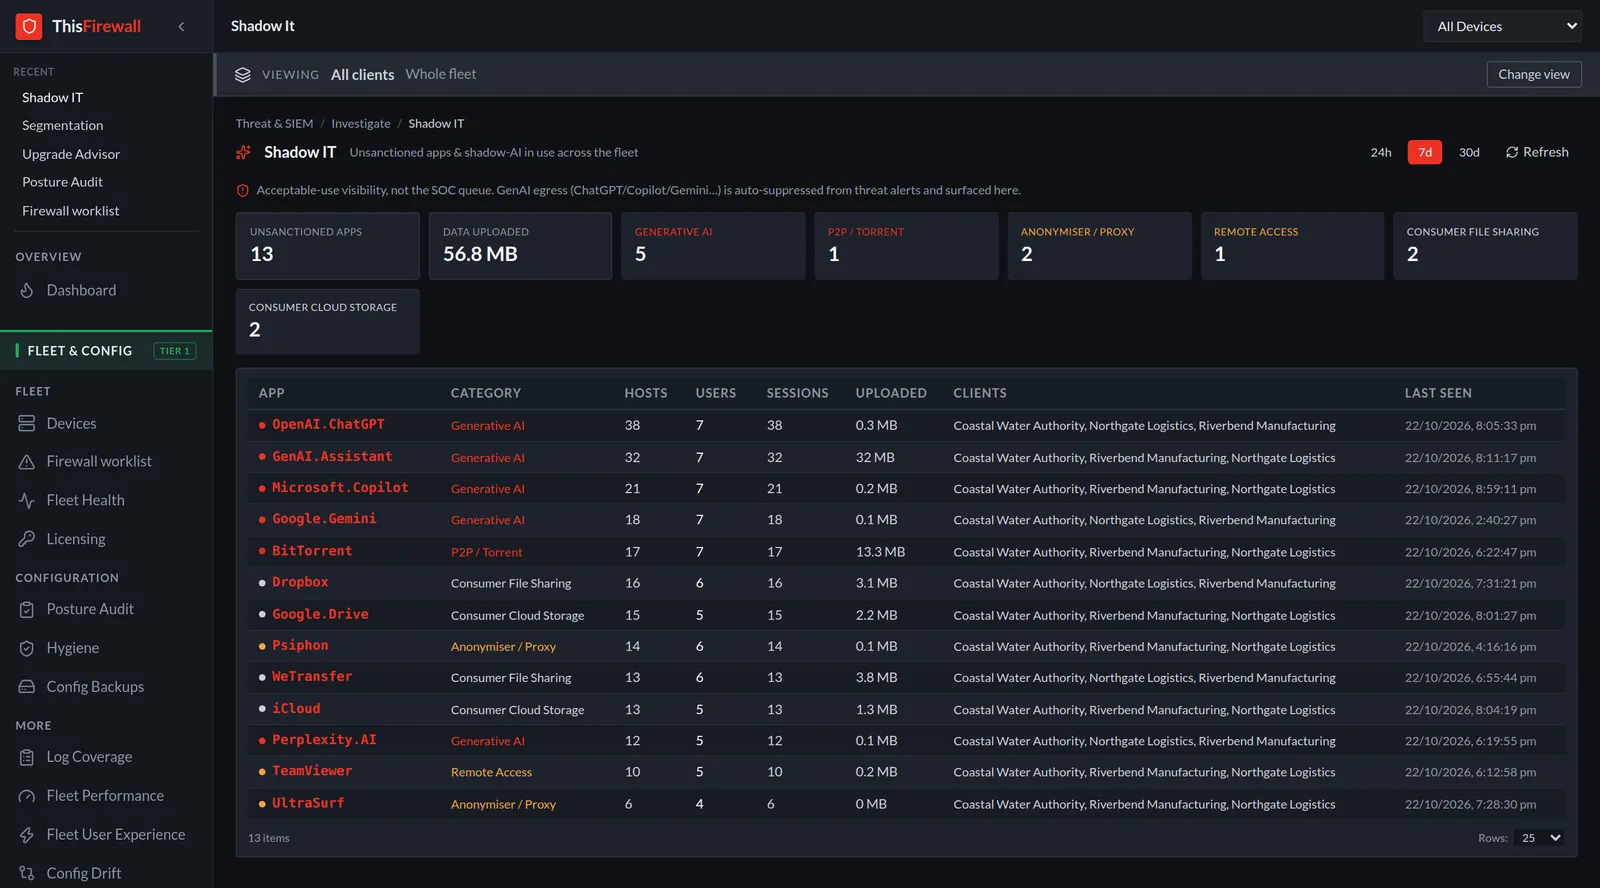
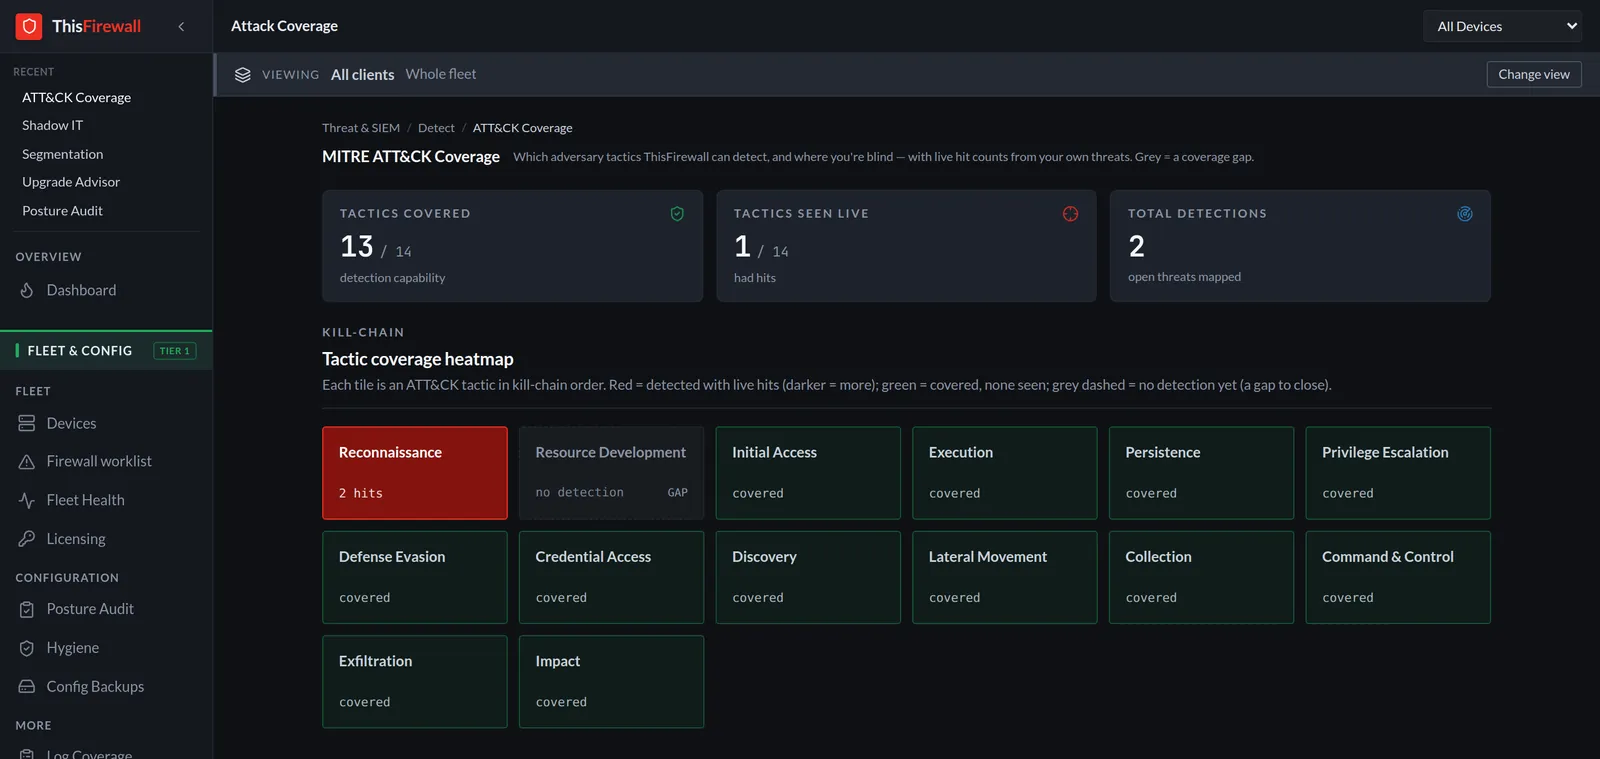
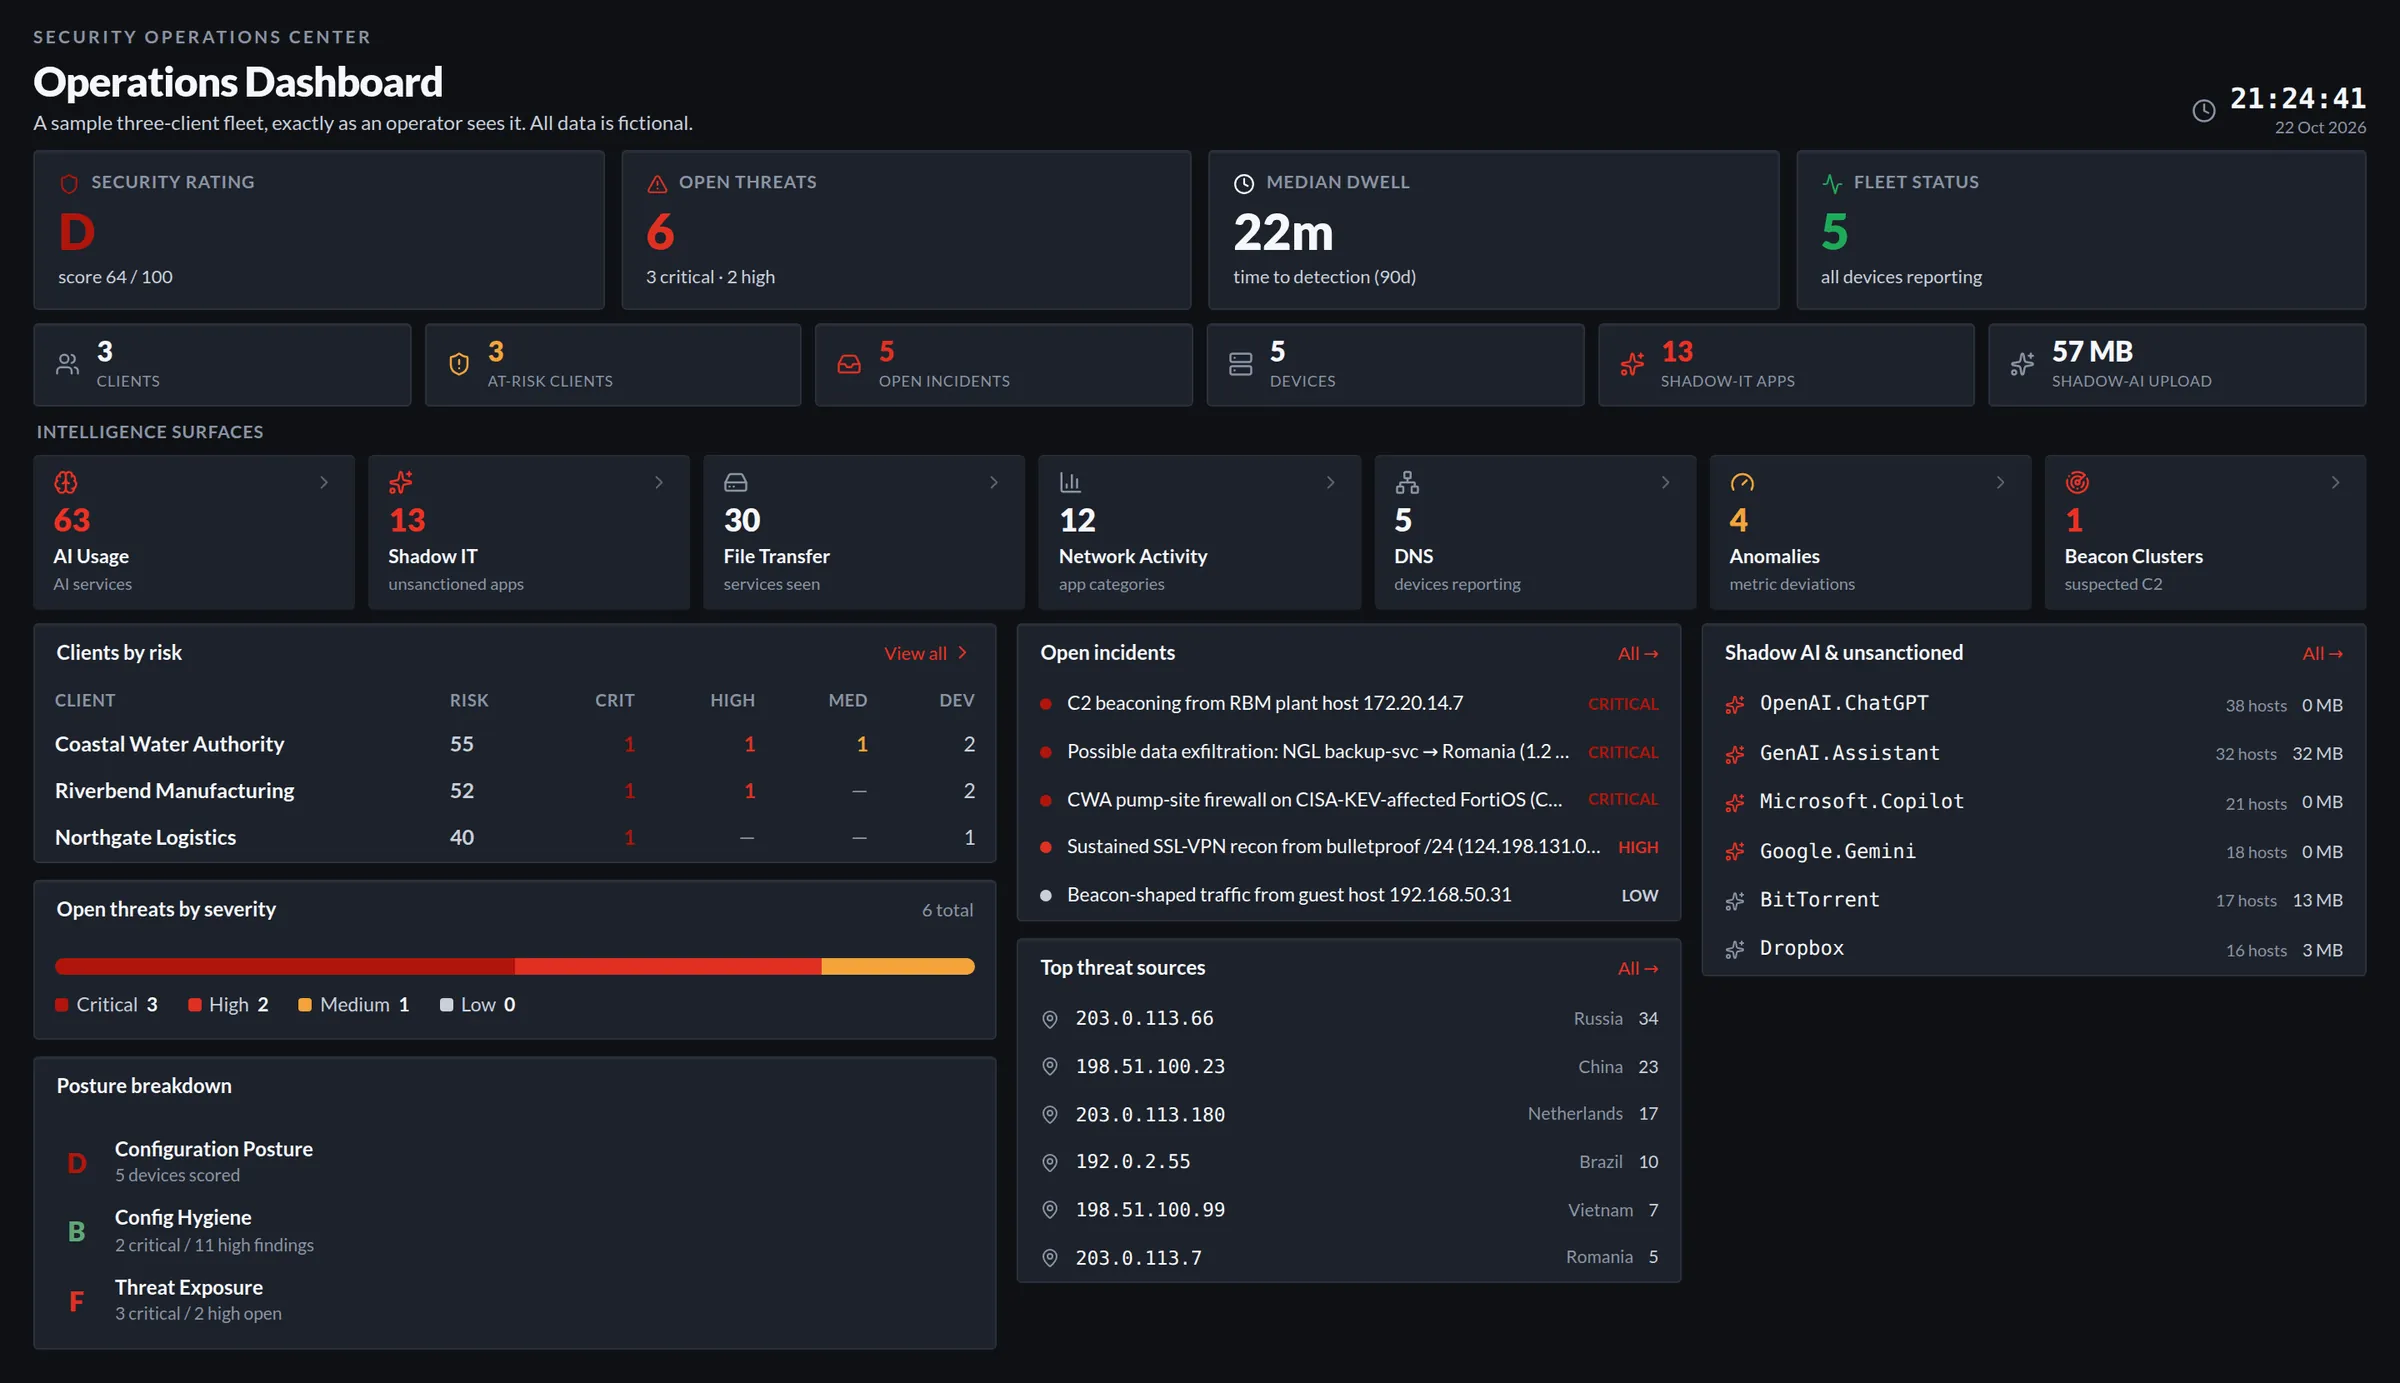
Every log is enriched with the IP's owner, country, application and user, then 21+ behavioural hunts run over it continuously: beaconing, brute force, exfiltration, reconnaissance and shadow IT.