Firewall security analytics · Proactive SOC

Your firewalls see the attack first. We make sure someone acts on it.

ThisFirewall reads every log your FortiGate fleet sends, checks each alert before it reaches a person, hunts every five minutes and opens the ticket with the evidence attached. When you want people watching too, Belton's SOC can take the queue.

  • Read-only toward your firewalls
  • No agents or sensors
  • Live in an afternoon
  • Built in New Zealand
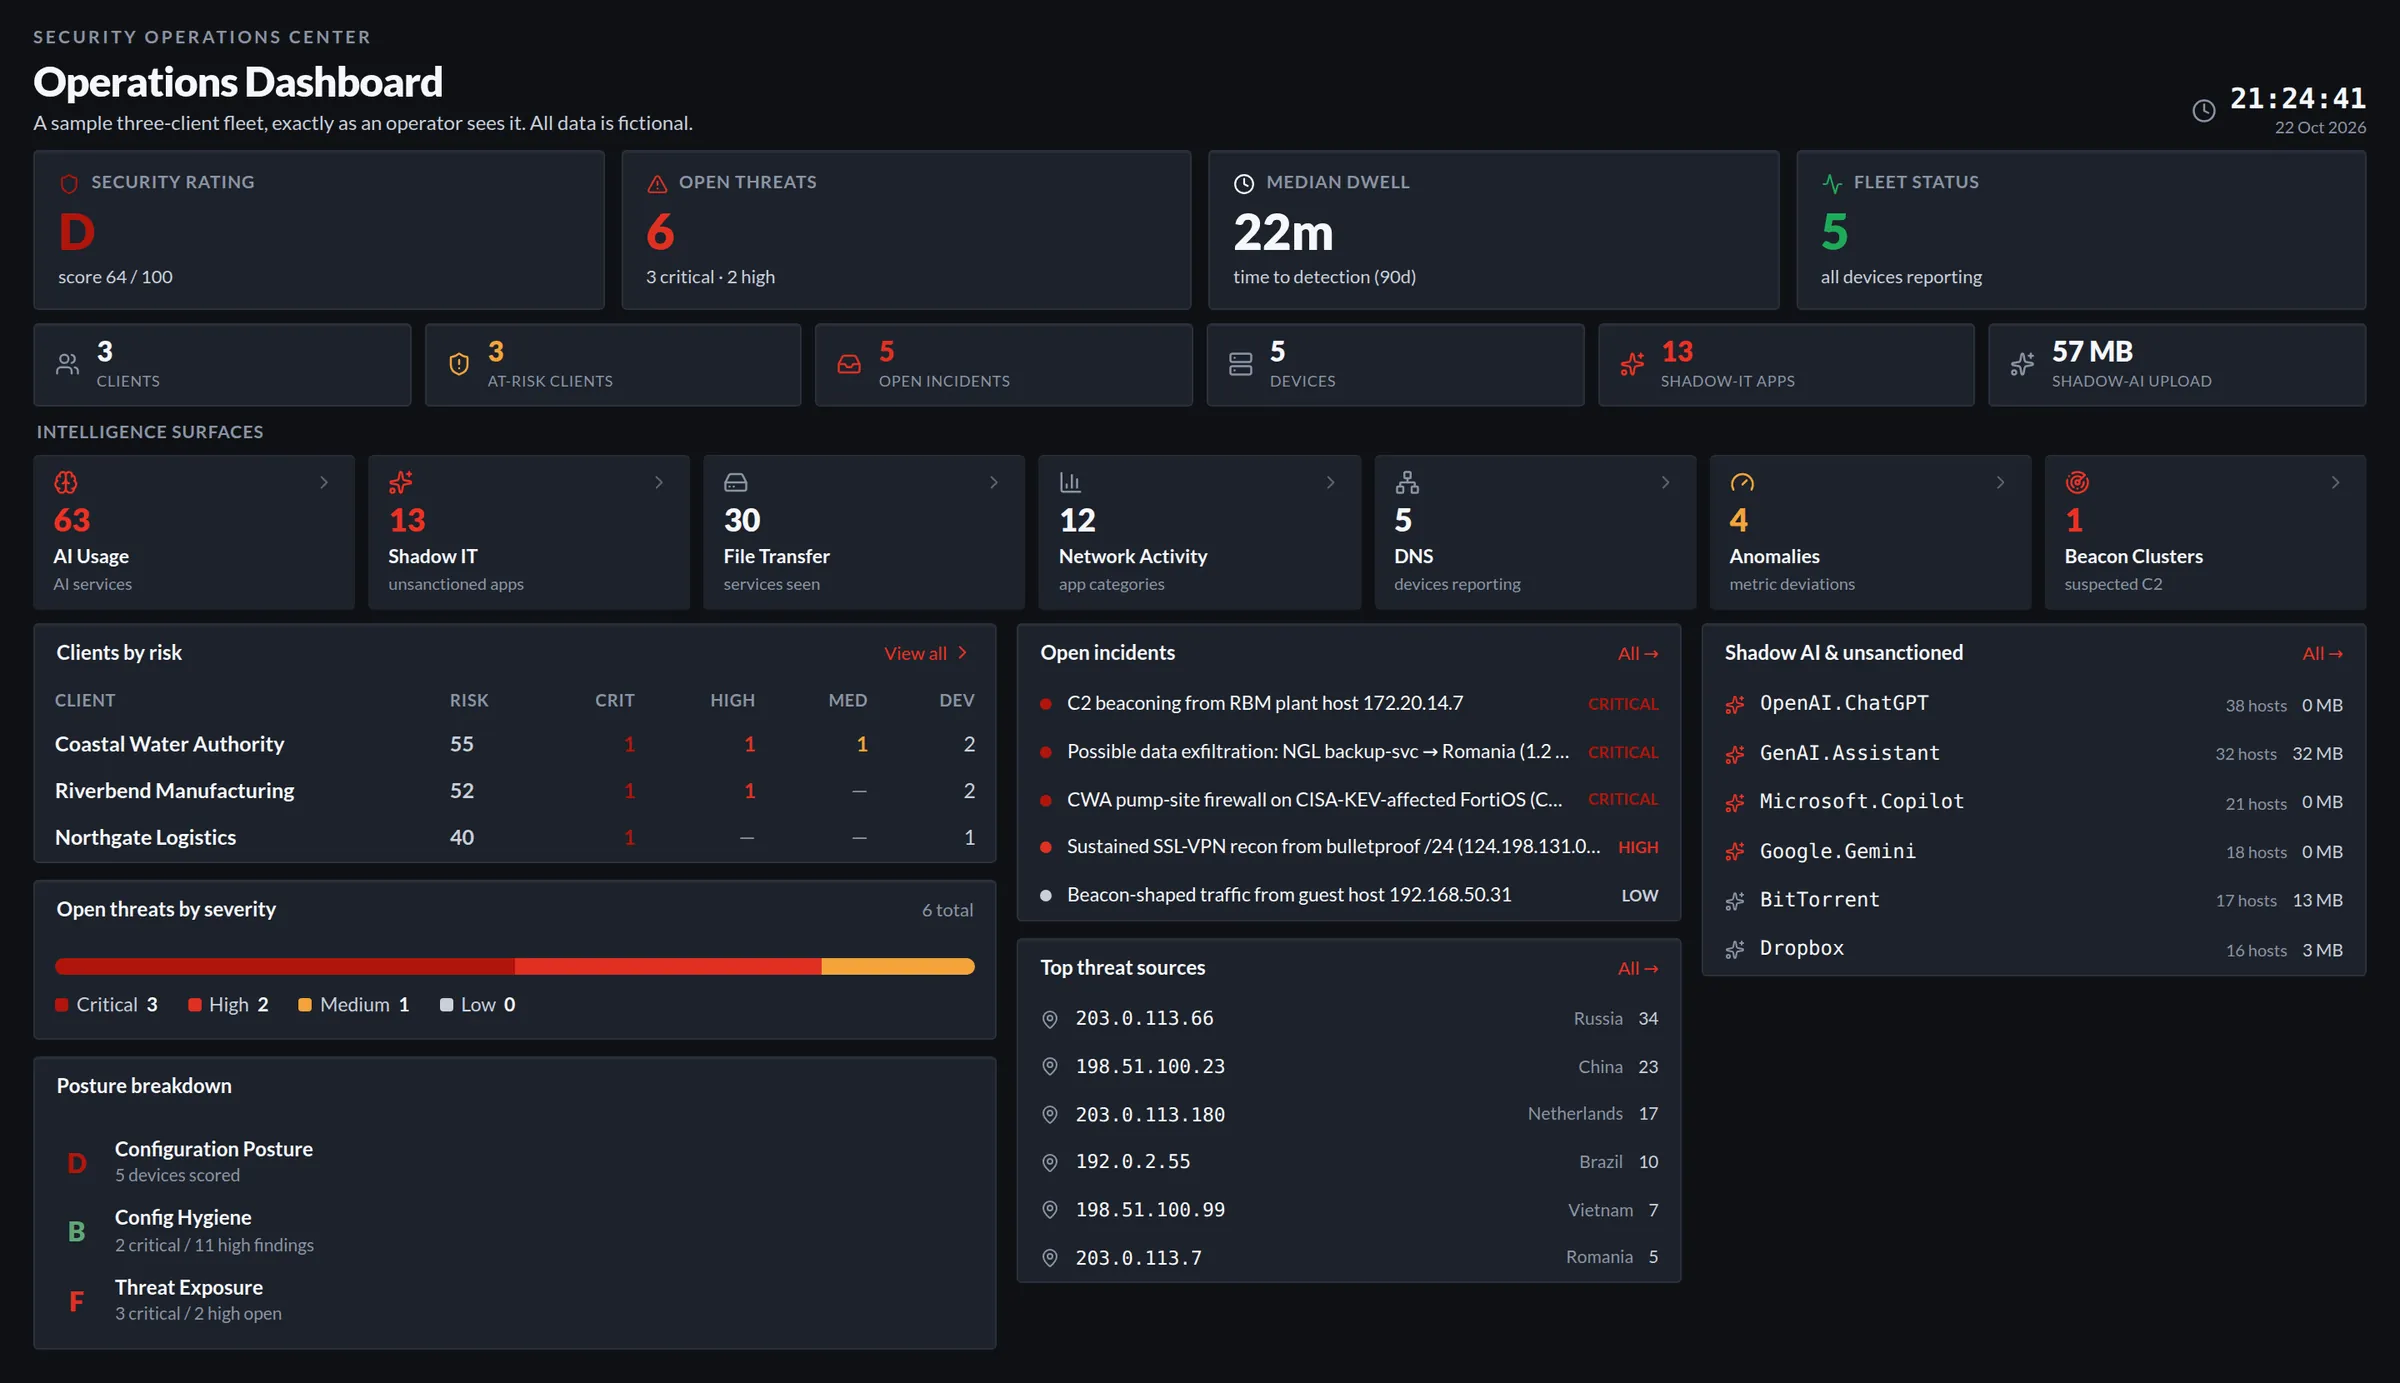
demo.thisfirewall.com/start View full size Operations Dashboard: security rating D, six open threats, median dwell time 22 minutes, clients ranked by risk, open incidents and shadow AI services across a fictional three-client fleet.
Operations Dashboard. The real console, running on a fictional three-client fleet.
Reads FortiGate today through FortiOS syslog and the REST API. More vendors are on the roadmap.
  • FortiGate
  • Palo Alto
  • Cisco
  • Sophos
  • Check Point
  • pfSense

The problems it solves

What goes wrong in a firewall estate, and what ThisFirewall does about it.

Built for MSPs, internal IT teams and SOCs that run FortiGate fleets and need more than a log viewer.

Nobody reads the logs.

Every firewall logs every session it handles. Across a fleet that is far more than anyone can read, so the connection your policy allowed sits there unread.

Every log is enriched with the IP's owner, country, application and user, then 21+ behavioural hunts run over it continuously: beaconing, brute force, exfiltration, reconnaissance and shadow IT.
Too many alerts, no verdicts.

Point tools raise everything and decide nothing. The alert that matters arrives with forty that don't.

Eight checks run before anything becomes an alert, including allowlists, threat intelligence, network ownership and the site's own baseline. Related signals become one case, and every host gets one verdict: clean, suspicious or compromised.

Config drift and lapsed licences.

Admin access without MFA, an over-permissive rule, a support contract that quietly expired. You find out in an audit or an outage.

Each firewall's configuration is scored against best practice and the CIS FortiGate benchmark, compared with the rest of the fleet, backed up and diffed. Licence and support expiry is tracked per device.

Firmware with known vulnerabilities.

Matching every vendor advisory to the exact build on every firewall is slow work, so it gets put off.

Firmware is matched against the NVD CVE catalogue, CISA's Known Exploited Vulnerabilities list and Fortinet PSIRT advisories, with an upgrade path to the recommended release.

Remote access under attack.

SSL-VPN portals are scanned and password-sprayed constantly, and a successful login from the wrong place looks like any other login.

Hunts every five minutes catch SSL-VPN brute force and tie failures to any later success. Command-and-control beacons are caught by their timing, even inside HTTPS.

Proving it to the board, the auditor or the client.

Everyone asks whether you are secure. A good answer needs evidence.

An A–F security rating, MITRE ATT&CK coverage, dwell time and control mapping to CIS, NZISM, ISO 27001 and NIST CSF, live in the console or as scheduled reports.

Proactive SOC

The night shift, already worked.

Most security tools wait for someone to look. ThisFirewall does the first hour of the investigation on its own, so whoever picks it up starts with a case already built.

  1. 02:14:07

    Allowed by policy

    A host on Riverbend Manufacturing's plant network opens an HTTPS session to an address in St Kitts. The firewall allows it. It is one line in a night of logs.

    RBM-EDGE-FW01 · 172.20.14.7 → 203.0.113.200:443 · action=accept
  2. 02:25:00

    The hunt notices the rhythm

    Hunts run over the fleet's traffic every five minutes. This one sees the same destination every 120 seconds, give or take two. People don't keep time like that. Malware does.

    c2_beaconing · interval 118–122 s · 6 sessions
  3. 02:25:02

    Checked before it becomes an alert

    Eight checks run first: not a private or reserved address, not on an allowlist, threat-intel and network-owner lookups, and this site's own baseline. The network was registered nine days ago, and this site has never talked to St Kitts before.

    validation 8/8 · network age 9 days · first contact: KN
  4. 02:25:03

    Four signals, one case

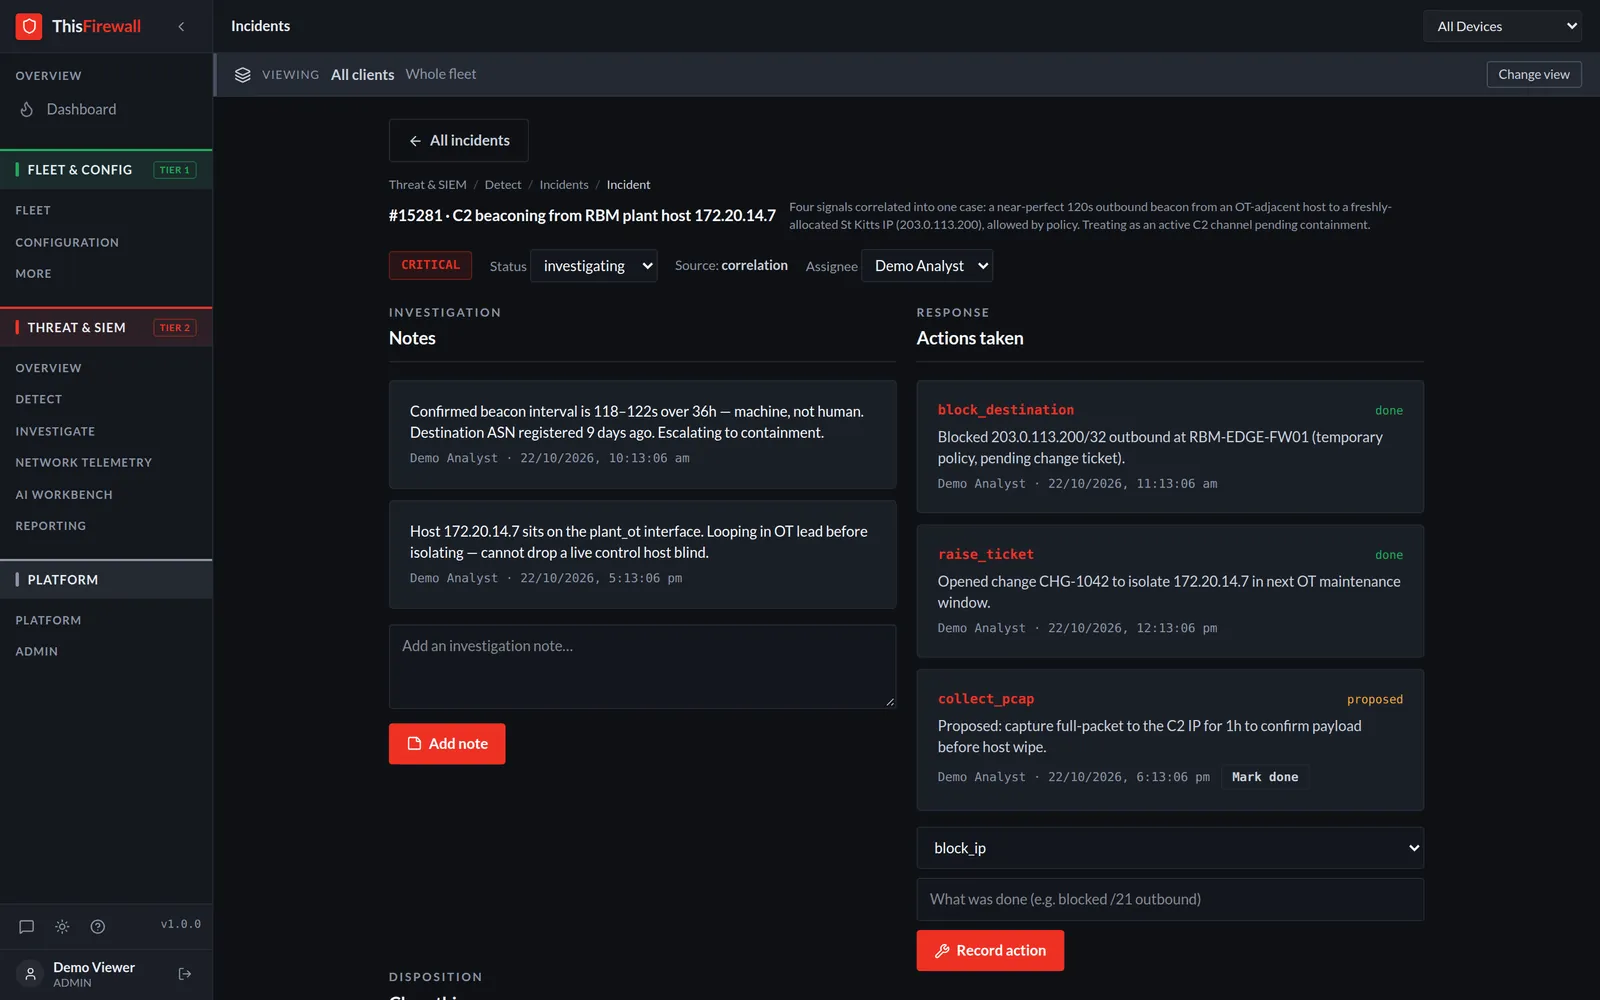
    The beacon, the new network, the new country and the plant-network location are joined into a single case, scored critical, with the evidence attached.

    case #15281 · CRITICAL · C2 beaconing from RBM plant host
  5. 02:26:40

    The investigation starts without you

    An AI investigator reviews the case. When it is confident the activity is malicious, it opens a critical ticket in Autotask with the timeline and evidence.

    verdict=malicious · ticket → Autotask (critical)
  6. 07:40

    A person makes the call

    The engineer on shift, yours or Belton's, starts with one case instead of a night of logs. They block the destination at the edge as a temporary rule and raise a change to isolate the host in the next OT maintenance window, because you don't drop a live control host blind.

    block 203.0.113.200/32 @ RBM-EDGE-FW01 · CHG-1042 raised

A fictional case from the demo fleet. The times are illustrative; the screens are real.

demo.thisfirewall.com/incidents View full size Incident #15281, C2 beaconing from RBM plant host 172.20.14.7, marked critical and investigating, with analyst notes and the actions taken: destination blocked, change ticket raised, packet capture proposed.
The case. Four signals in one record, with the notes and every action taken.
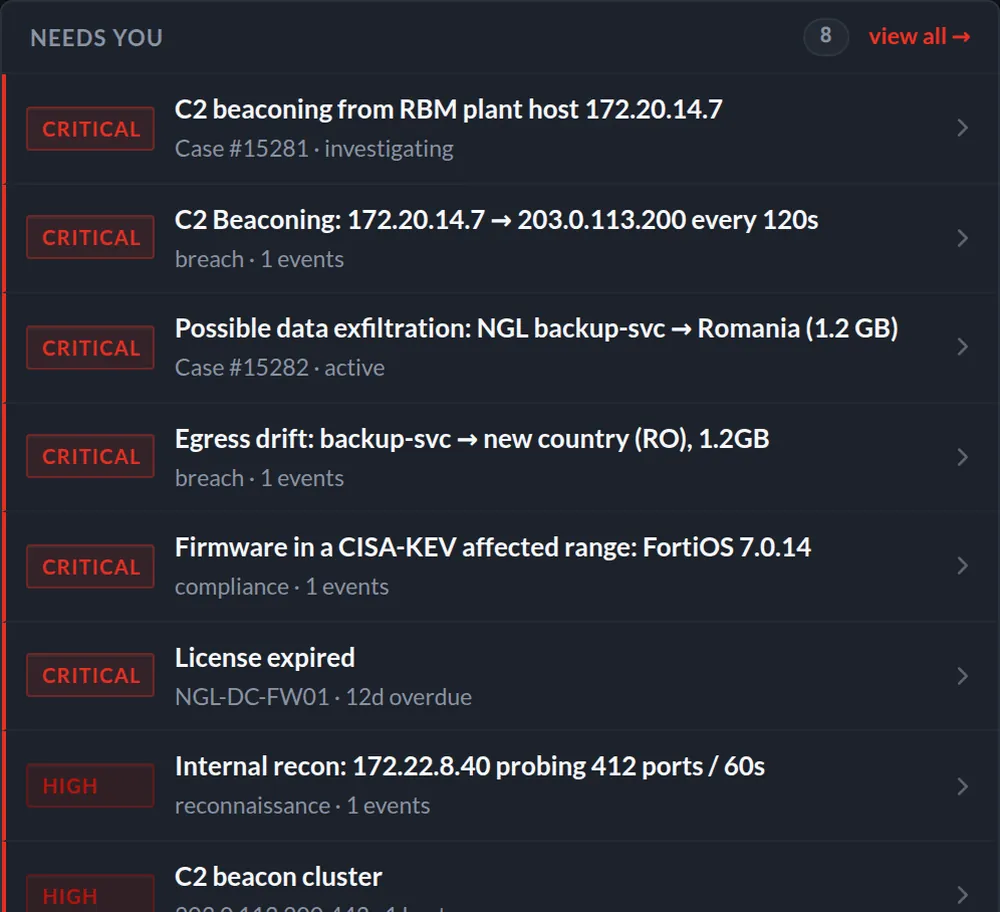
Needs you View The Command Center's Needs you queue, worst first: C2 beaconing, possible data exfiltration, egress drift, firmware in a CISA-KEV affected range, an expired licence and internal reconnaissance.
The queue. Worst first, across every client.
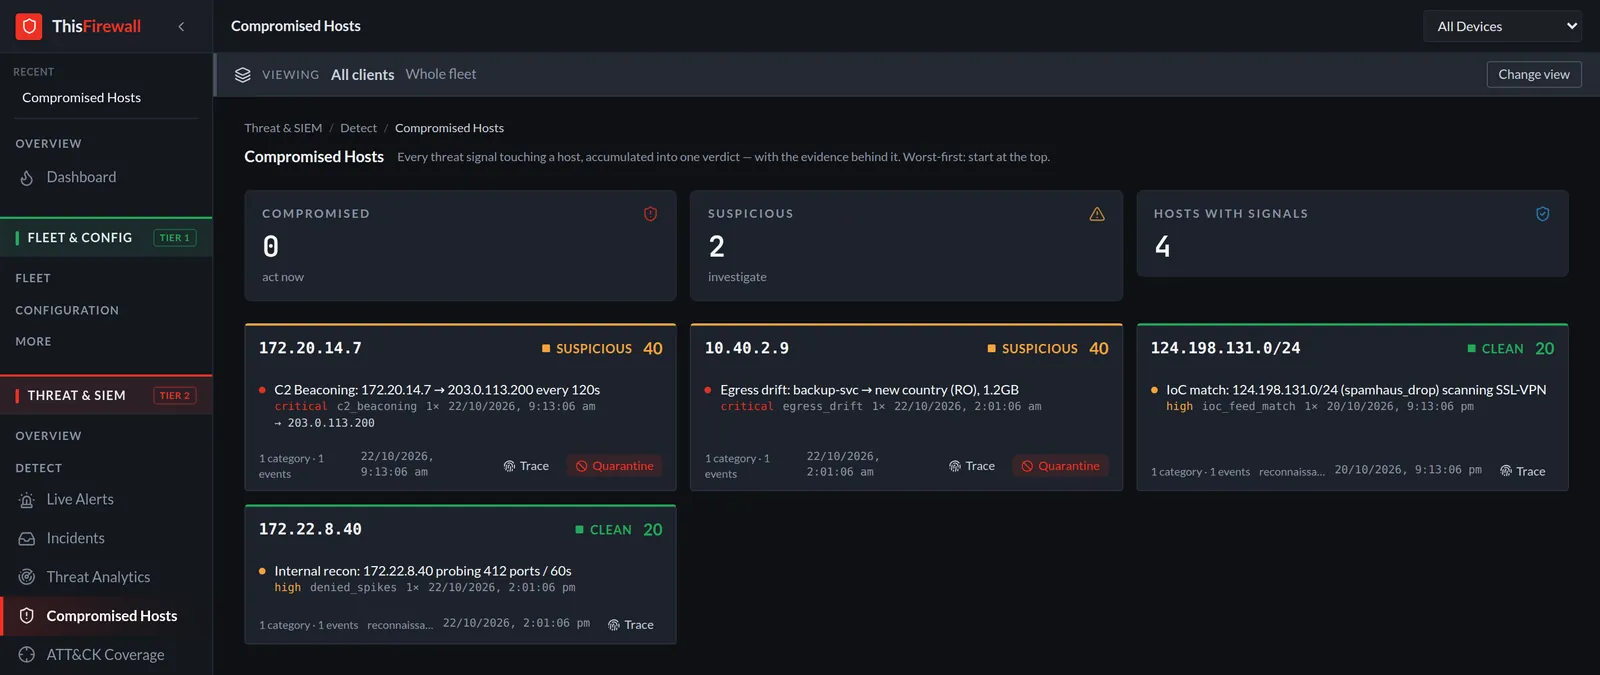
Compromised Hosts View Compromised Hosts verdict card for 172.20.14.7: suspicious, score 40, from C2 beaconing to 203.0.113.200 every 120 seconds, with Trace and Quarantine actions.
The verdict. One answer per host, with the evidence.
In every plan

The platform works the queue

It runs on every firewall, day and night, without anyone watching.

  • 21+ behavioural hunts, run every five minutes
  • Eight checks before anything becomes an alert
  • Related signals correlated into cases, with dwell time measured
  • AI investigation on your own key or a local model, if you want it
  • Critical tickets in Autotask, with status synced back
  • Fleet health that notices when a firewall goes quiet, and suggests why
  • Fixes proposed as review-only CLI, never pushed to your firewalls
Optional add-on

Add Belton's SOC

Belton IT Nexus, the New Zealand company behind ThisFirewall, can run the queue for you. Belton analysts triage your cases, follow up the tickets and bring you the decisions that need a person.

Scope and coverage are agreed with you and quoted separately.

Ask about the managed SOC

Product tour

The real console, on a fictional fleet.

Every screen here comes from the read-only demo: three made-up clients, five firewalls, and the kind of trouble real networks have.

Detect

Live alerts, triaged before you see them.

One queue for every firewall and every client, worst first. Each alert shows what was seen, where, how often and which checks it passed, so the first decision is quick.

Also hereIncidents · Compromised Hosts · Beacon Clusters · Anomalies · Dwell Time · Threat Hunting · SSL VPN Exposure

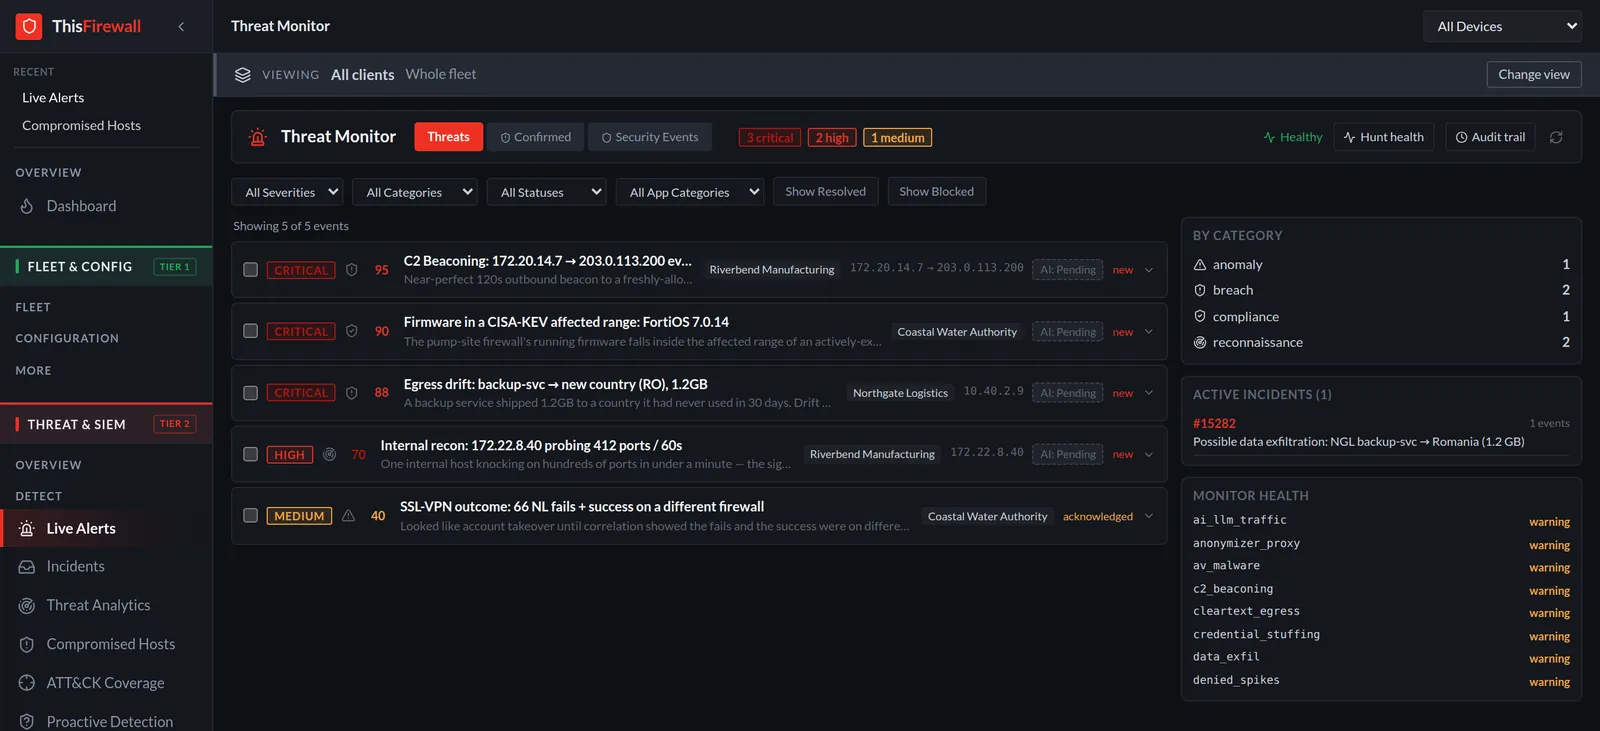
demo.thisfirewall.com/threat-monitor View full size Threat Monitor listing live alerts across the fleet: C2 beaconing, firmware in a CISA-KEV affected range, egress drift to a new country, internal reconnaissance and an SSL-VPN success after failures.
Live Alerts. Every firewall and client in one triage queue.
Investigate

See what is actually on the wire.

Traffic by category, unsanctioned apps and AI services, DNS, file transfer and destinations by country. Trace any IP or host across the whole fleet from one search box.

Also hereThreat Map · DNS · Log Search · IP / Host Trace · Egress Intel · File Transfer

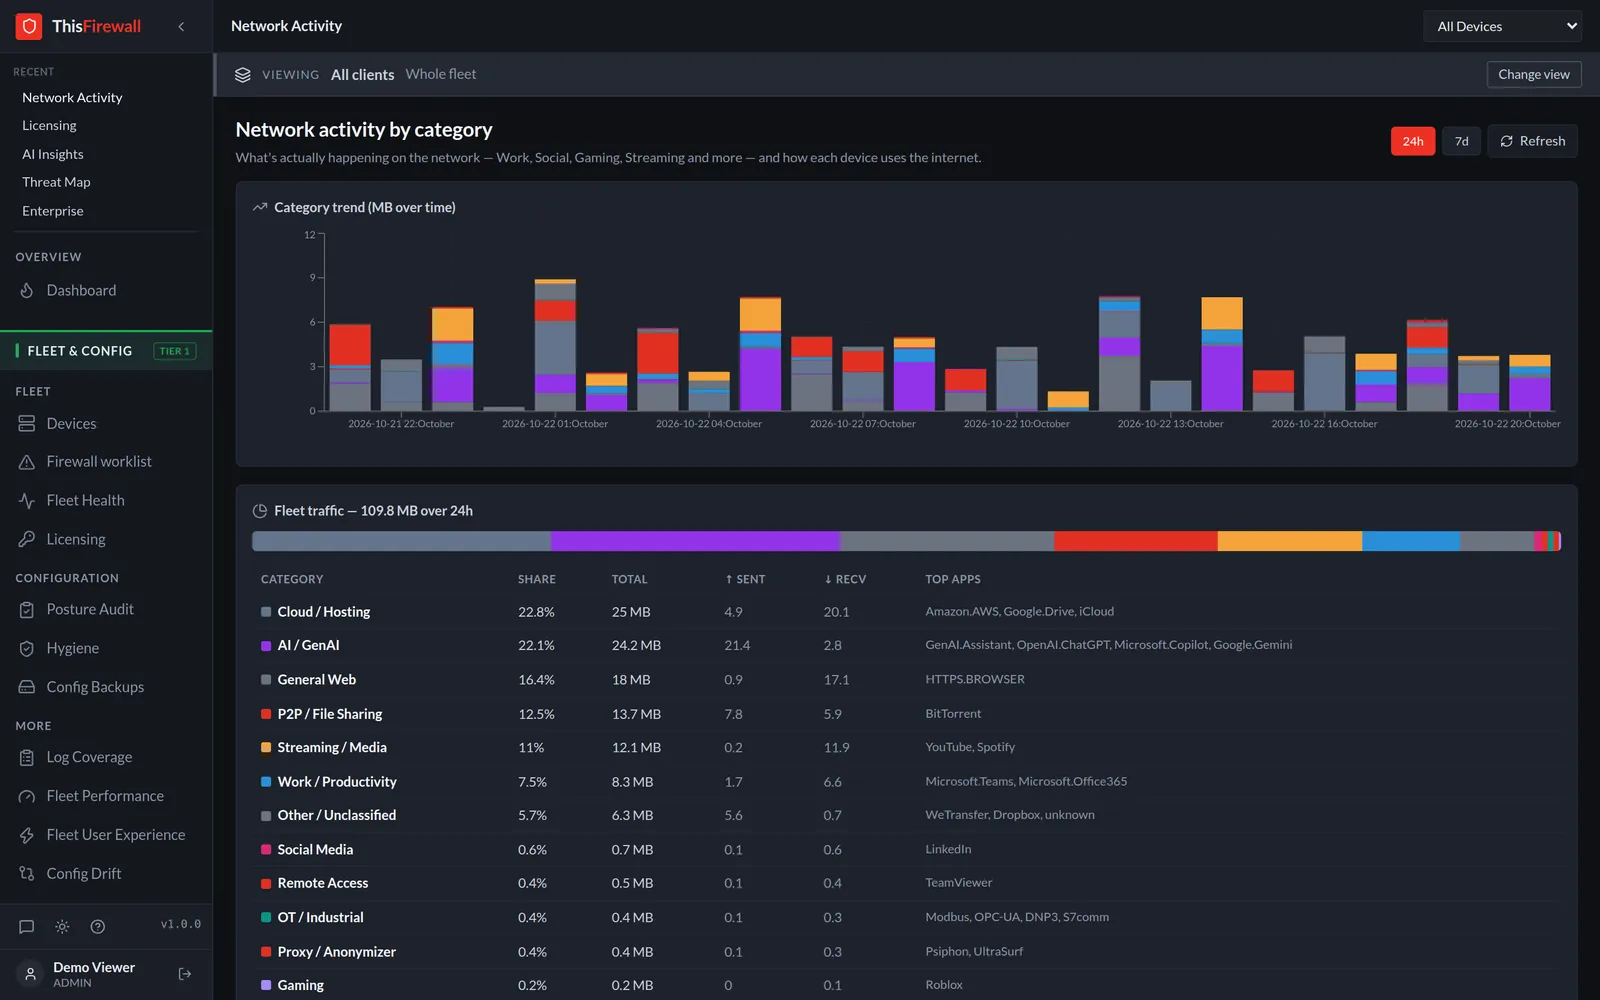
demo.thisfirewall.com/network-activity View full size Network Activity: fleet traffic broken down by category over time, including cloud, AI services, peer-to-peer, streaming and OT industrial traffic.
Network Activity. What the fleet's traffic is, by category.
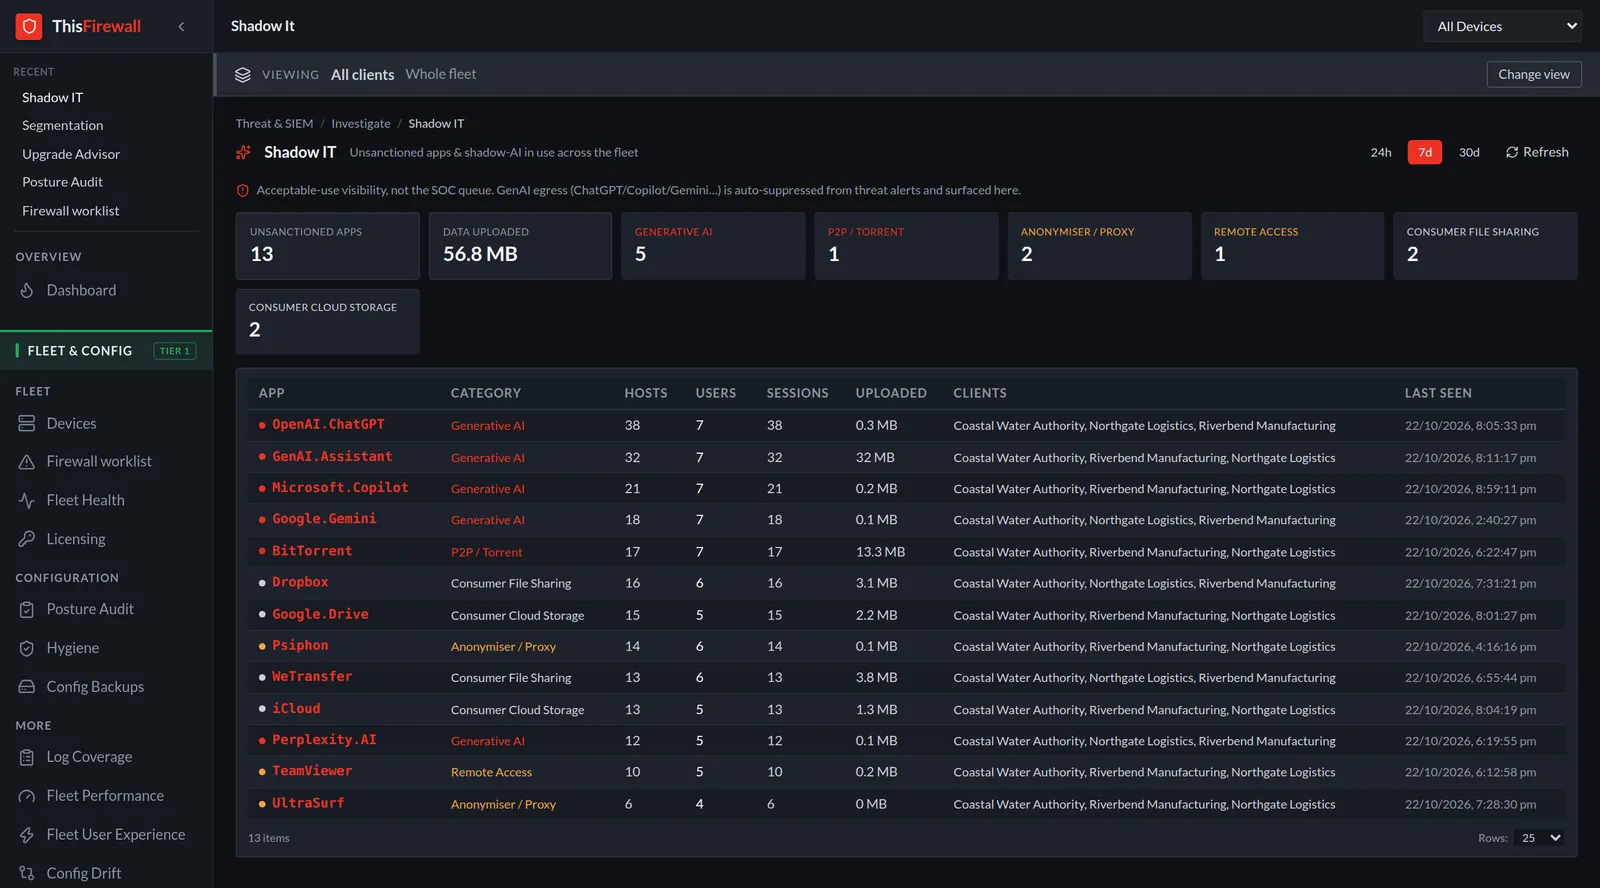
demo.thisfirewall.com/shadow-it View full size Shadow IT: unsanctioned apps and AI services seen on the network, with hosts, users, sessions and data uploaded per app.
Shadow IT and AI. Which unsanctioned services are in use, and how much data went to them.
Harden

Keep every firewall configured, licensed and patched.

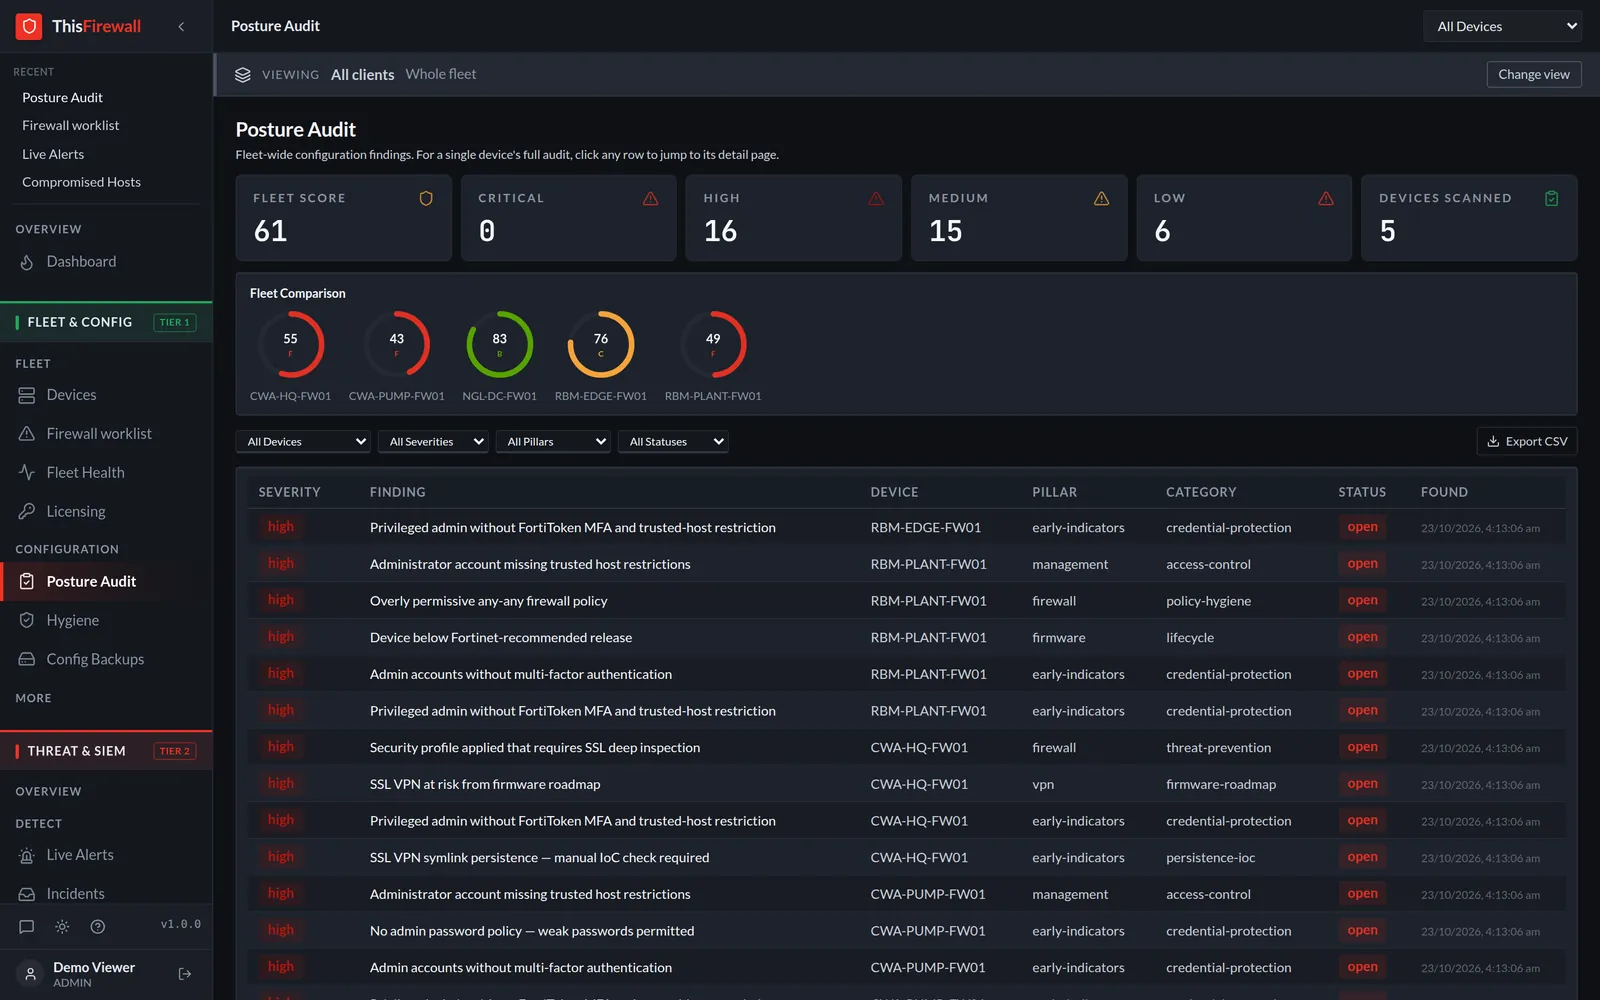
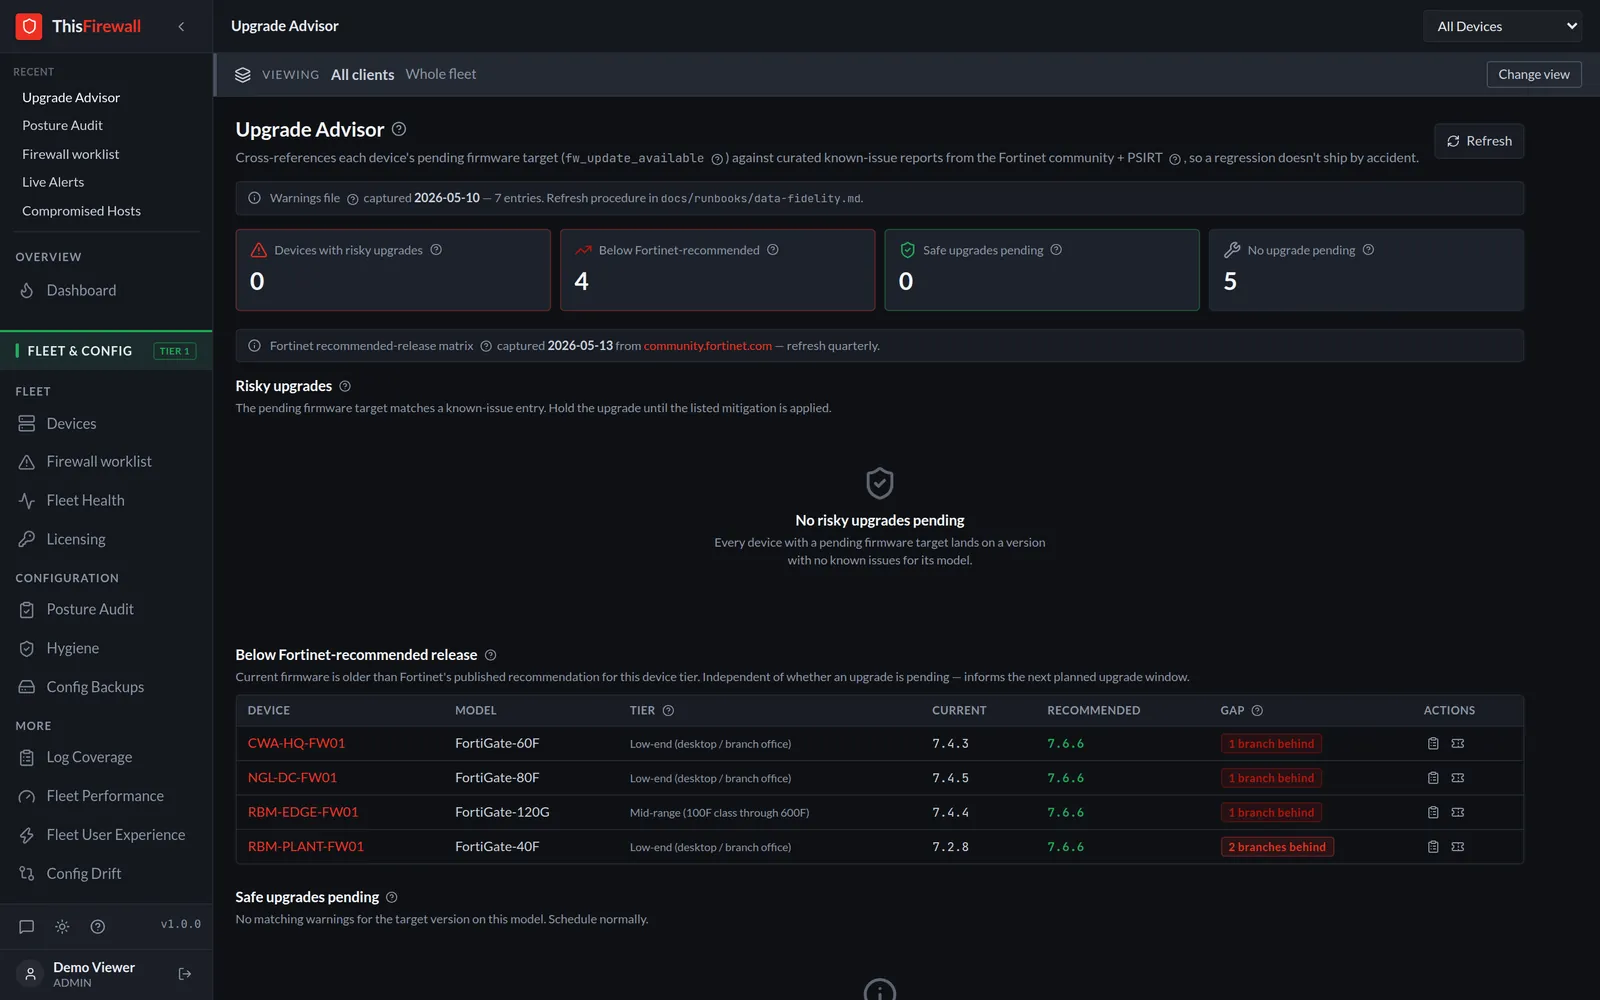
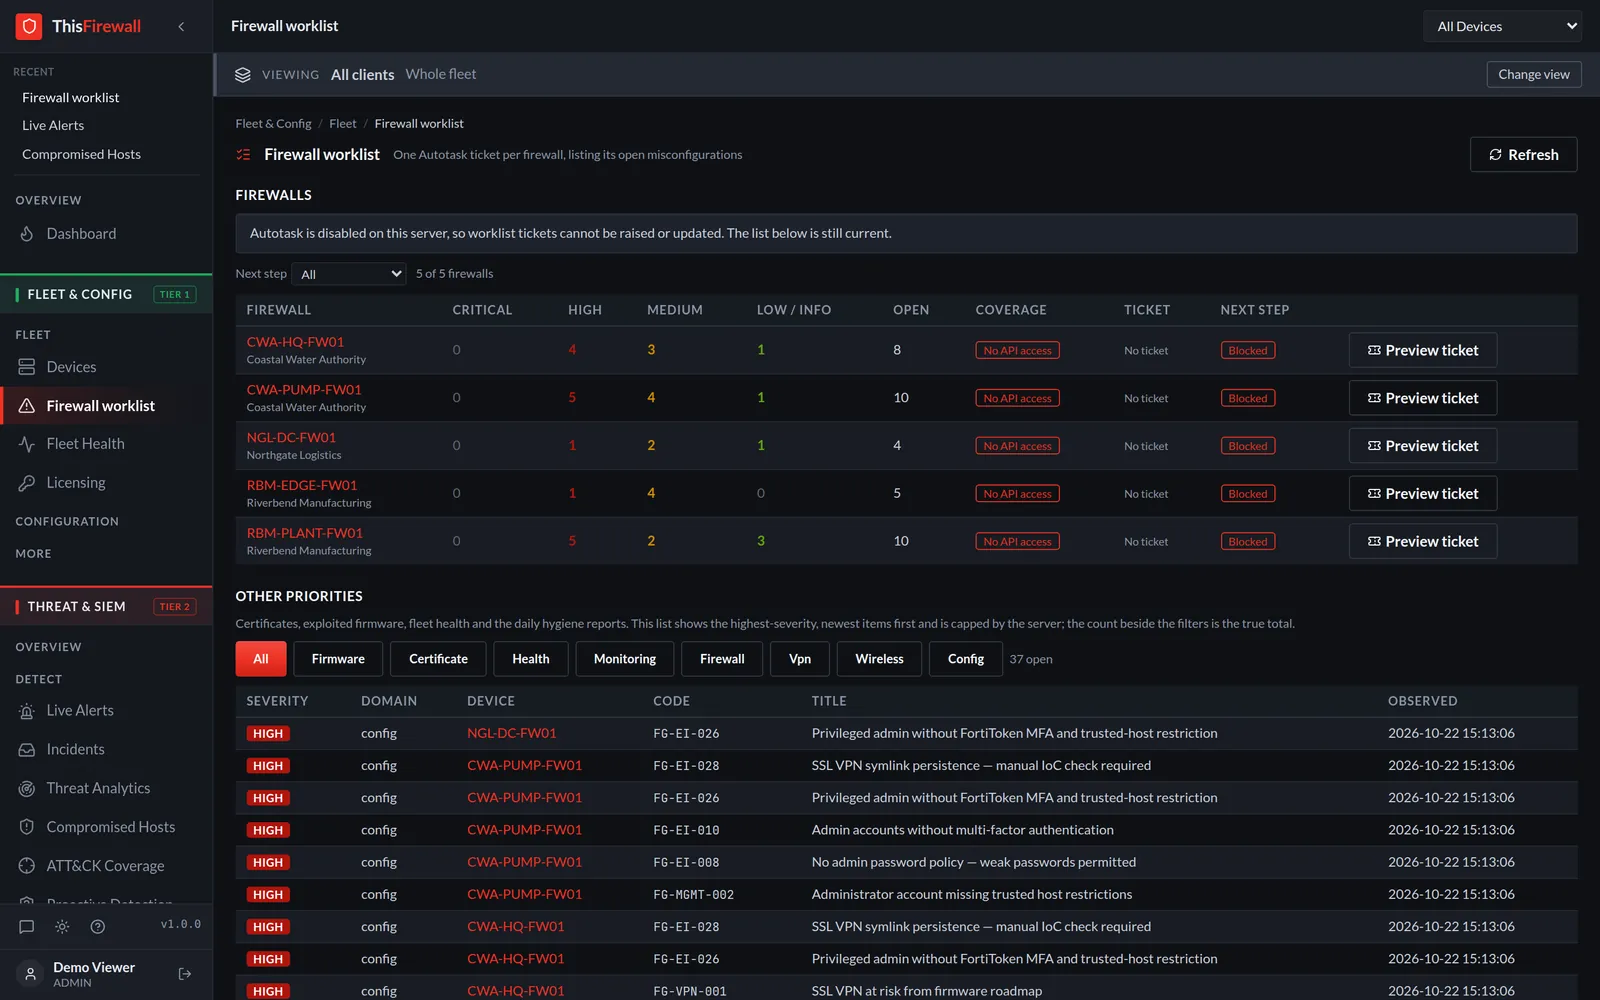
Posture findings for every device, fleet-wide standardisation, firmware measured against Fortinet's recommended release, and a worklist that turns each firewall's open findings into one ticket.

Also hereLicensing · Standardisation · Config Backups · Config Drift · Policy Analyzer · CVE Exposure

demo.thisfirewall.com/posture View full size Posture Audit: a fleet score of 61, findings by severity, a per-device score comparison and a list of configuration findings such as admin access without MFA.
Posture Audit. Configuration findings for every firewall, scored and ranked.
Upgrade Advisor View Upgrade Advisor: firewalls running below the Fortinet-recommended release, with the current and recommended versions.
Upgrade Advisor. Firmware against the recommended release.
Firewall worklist View Firewall worklist: each firewall's open findings counted by severity, with a ticket preview per device and other priorities listed below.
Firewall worklist. One Autotask ticket per firewall.
Segment

Know exactly what crosses into OT.

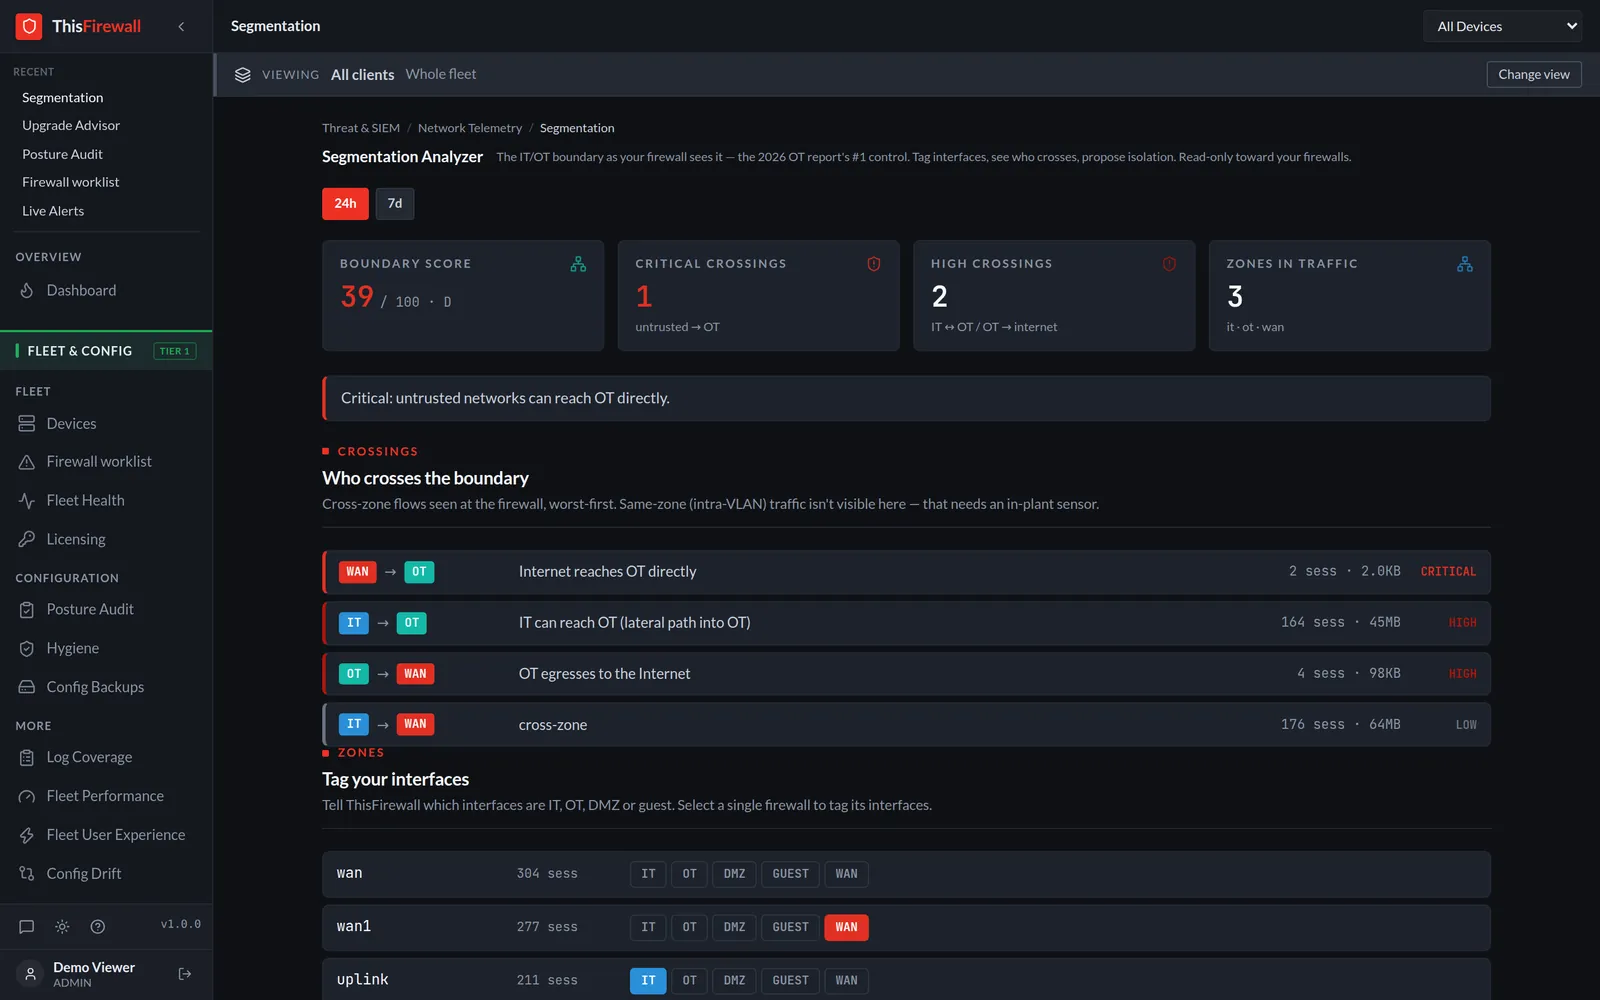
Tag interfaces as IT, OT, DMZ or guest and the segmentation view shows every crossing, scored, with the critical paths first. OT maturity is graded on the L0 to L4 ladder from traffic actually observed, not from a questionnaire.

Also hereOT Maturity · Traffic · VPN · WAN / SD-WAN

demo.thisfirewall.com/segmentation View full size Segmentation Analyzer: a boundary score, a critical warning that untrusted networks can reach OT directly, and the list of zone crossings such as internet to OT and IT to OT.
Segmentation. Every IT/OT crossing, scored, critical paths first.
Prove

Evidence for the board, the auditor and the client.

An executive scorecard, an A–F security rating, ATT&CK coverage and dwell time, with controls mapped to CIS, NZISM, ISO 27001 and NIST CSF. Schedule the reports and they arrive on their own.

Also hereSecurity Rating · Dwell Time · Scheduled Reports · Client Reports

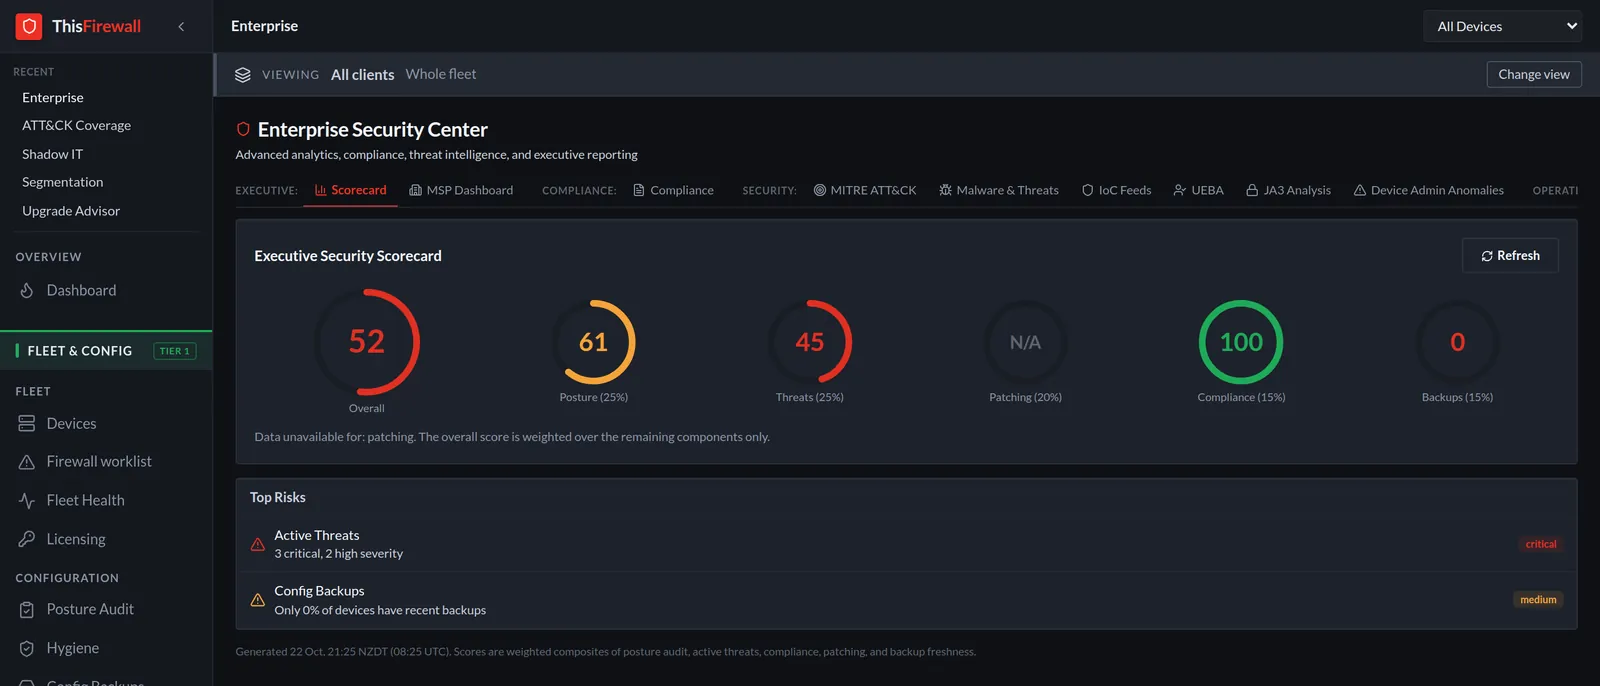
demo.thisfirewall.com/enterprise View full size Enterprise Security Center: an executive scorecard with overall, posture, threat, compliance and backup scores, and the top risks listed below.
Executive scorecard. The one page the board reads.
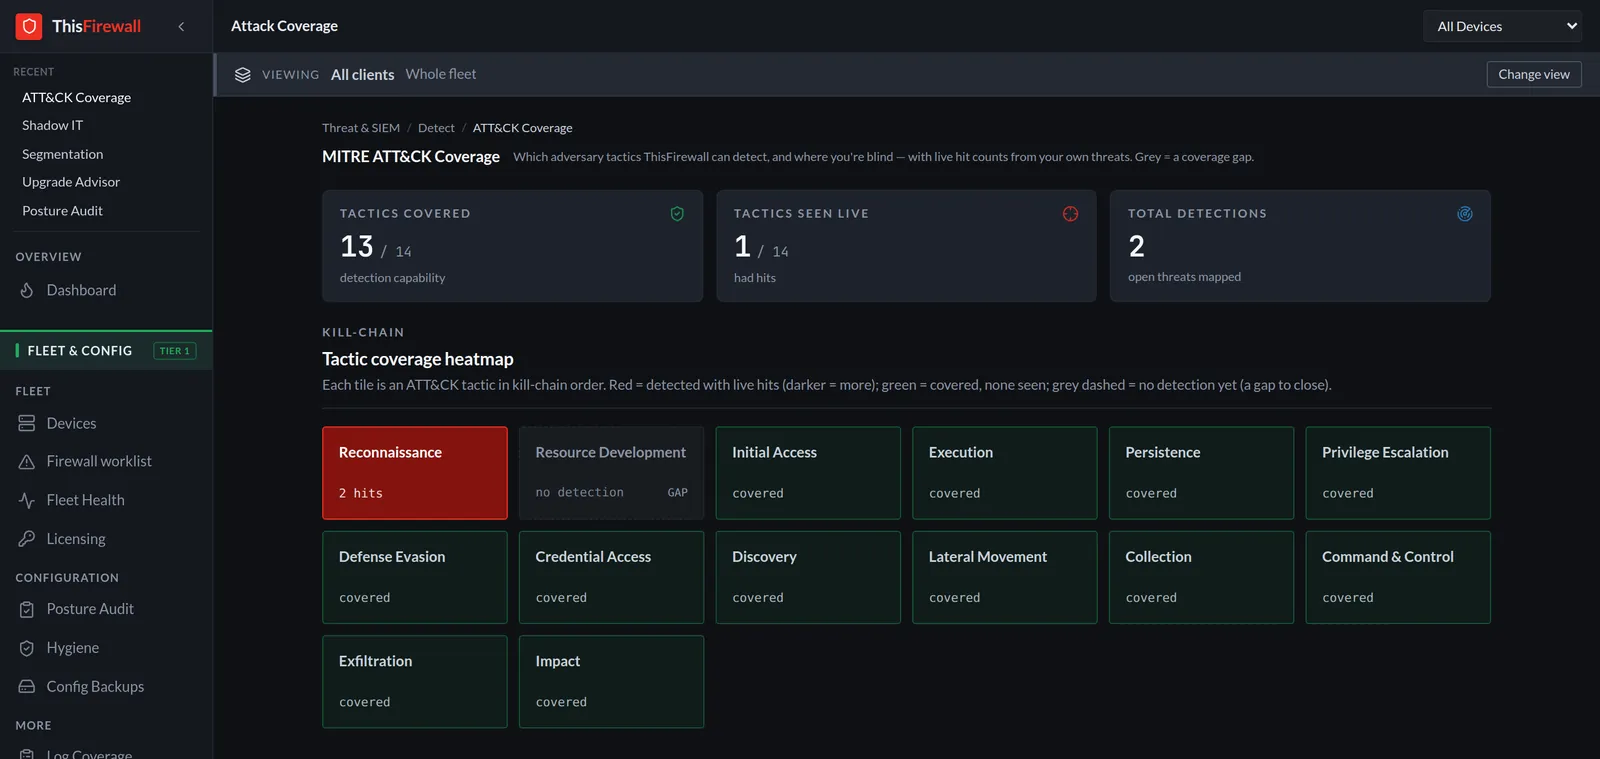
demo.thisfirewall.com/attack-coverage View full size MITRE ATT&CK coverage: tactics covered by detections, tactics seen live, and a heatmap of the kill chain.
ATT&CK coverage. What the detections cover, and what has actually been seen.

How it works

Live in an afternoon.

No agents, no span ports, no new hardware. Two settings on each firewall.

  1. Send syslog

    Point each FortiGate's syslog at ThisFirewall, over TLS on 6514 or UDP on 514.

  2. Add a read-only API user

    ThisFirewall reads configuration, licences, firmware and health through it. It never writes to your firewalls.

  3. Let it work

    Dashboards fill from the first log, hunts start straight away, and posture, licensing and firmware are scored on the first scan.

Fleet & Config TIER 1

Works from the read-only API alone: inventory, posture, standardisation, licensing, firmware and fleet health from day one.

Threat & SIEM TIER 2

Lights up as logs arrive: hunting, cases, traffic, shadow IT, segmentation, dwell time and the proactive SOC. Both layers are in every plan.

Managed by Belton

We host, patch, monitor and back it up. Shared with a database per tenant, or a dedicated single-tenant instance.

Self-hosted

Docker on Ubuntu 24.04 LTS, in your cloud or on-prem. Around 4 vCPU and 16 GB RAM, plus storage for your retention.

In your region

New Zealand, Australia, the EU or your own. Your data stays in the region you choose.

Pricing · Introductory rates

One platform fee, then a price per firewall.

Introductory rates for our first customers. The platform fee covers everything ThisFirewall does. Each firewall is then priced by the size of your fleet, so the rate drops as you grow. Never per seat.

Platform

The whole platform, every feature

The console, continuous hunting, the proactive SOC automation, reporting and compliance evidence, for every client and site you run.

NZ$500

per month, excl. GST

plus, for every firewall

Small

1–5 firewalls

NZ$55

per firewall / month, excl. GST

A single site or a handful of branches.

Request a demo

Scale

26–100 firewalls

NZ$30

per firewall / month, excl. GST

An established MSP or SOC fleet.

Request a demo

Fleet

101+ firewalls

NZ$20

per firewall / month, excl. GST

A large MSP, enterprise or national SOC.

Talk to us

How it adds up

Your whole fleet is priced at the rate for its size. Examples, per month excl. GST:

  • 5 firewallsNZ$775
  • 12 firewallsNZ$1,004
  • 60 firewallsNZ$2,300
  • 150 firewallsNZ$3,500

Every feature is in every plan: threat detection and hunting, incident cases, egress and shadow AI, identity risk, fleet health, OT visibility, configuration posture, firmware exposure, dwell time and compliance evidence. Pay annually and save around 25% more.

Quoted separately

  • Hosting: self-hosted, managed by Belton, or a dedicated instance in your region
  • Belton's managed SOC, if you want people on the queue

Security and trust

Built to be trusted with your security data.

Read-only, propose-only

Syslog in and a read-only API user. Nothing is pushed back. Fixes arrive as CLI for your own change window.

Your logs stay put

Raw logs never leave your instance. Threat-intel lookups send only public IPs and indicators.

Encrypted where it counts

TLS 1.2 or 1.3 in transit, including syslog over TLS. Credentials and API keys encrypted at rest with AES-256-GCM.

Single sign-on and audit

Microsoft Entra ID sign-in, access scoped per client and site, and a hash-chained audit trail of who saw what, from where.

AI is optional

Bring your own OpenAI or Anthropic key, or run a local model. Prompts are sanitised and scoped to your tenant, and no model trains on your data.

Aligned to the frameworks

Engineered to ISO 27001 and SOC 2 principles and the New Zealand Privacy Act 2020.

Read the security page · Read the technical overview

Questions

The questions operators ask first.

Commercial

Does ThisFirewall touch or change my firewall?

No. It is read-only toward your firewalls. Policy changes come as review-only CLI that you apply yourself, in your own change window.

Do I need new hardware or agents?

No sensors, no agents, no span ports. ThisFirewall ingests the syslog you already send and reads through a read-only API user.

Which firewalls do you support?

FortiGate today. Palo Alto, Cisco, Sophos, Check Point and pfSense are on the roadmap. Tell us what you run and we will tell you where it sits.

Is there a human SOC, or just software?

The platform does the first pass on its own: hunts, checks, correlation, AI investigation and tickets. If you want people on the queue too, Belton IT Nexus offers a managed SOC on top, scoped with you and quoted separately.

Where does my data live?

On infrastructure we agree with you, including a dedicated single-tenant instance in your region. Your data stays yours.

How fast can we be live?

An afternoon for the first firewall: point syslog at ThisFirewall, add a read-only API user, and the dashboards fill from day one.

Can it see inside my industrial protocols?

It sees OT traffic crossing zones at the firewall, which is what segmentation governs. Deep inspection of function codes needs a sensor inside the plant, and we are clear about that line.

Is the introductory pricing permanent?

These rates are for the customers who join us first, while we onboard early deployments. Ask us for the specifics before you commit to a term.

Technical

What does it run on?

Ubuntu 24.04 LTS under Docker. A single instance runs comfortably on about 4 vCPU and 16 GB RAM, plus block storage sized to your log volume and retention.

What leaves my network?

Your raw logs never leave your instance. Outbound calls are limited and disclosed: Microsoft Entra ID for sign-in, optional AI on your own key with sanitised prompts, and threat-intel feeds that receive only public IPs and indicators.

How is data secured?

TLS 1.2 or 1.3 in transit, including syslog over TLS on 6514. Credentials and API keys are encrypted at rest with AES-256-GCM. The log store listens only on the local machine.

How are customers kept apart?

A database per tenant, with tenant-scoped access enforced on every read and write. A dedicated single-tenant instance is available.

How do sign-in and audit work?

Microsoft Entra ID single sign-on, role-based access scoped per client and site, and a tamper-evident, SHA-256 hash-chained audit trail of who saw what, from where.

Is AI required?

No. Bring your own OpenAI or Anthropic key, or run a local model. Prompts are sanitised, tenant-scoped and kept small, no model is trained on your data, and the platform is fully usable with AI turned off.

Full technical overview

Request a demo

See your own network in a 30-minute demo.

  • No new sensors, agents or hardware
  • Read-only and propose-only toward your firewalls
  • A walkthrough with an engineer
  • A clear per-firewall quote and a pilot you can scope

Prefer email? [email protected] · A Belton IT Nexus product.

Not ready for a demo?

Ask for a free Firewall Exposure Check. Point one firewall at ThisFirewall for 24 hours, or send us a config export, and we will return a report and walk you through it in 30 minutes.

Ask for an Exposure Check

Tell us about your estate

We use your details only to respond to this request. No spam, no list-selling. See our privacy policy.